Have the evidence ready before the lab asks
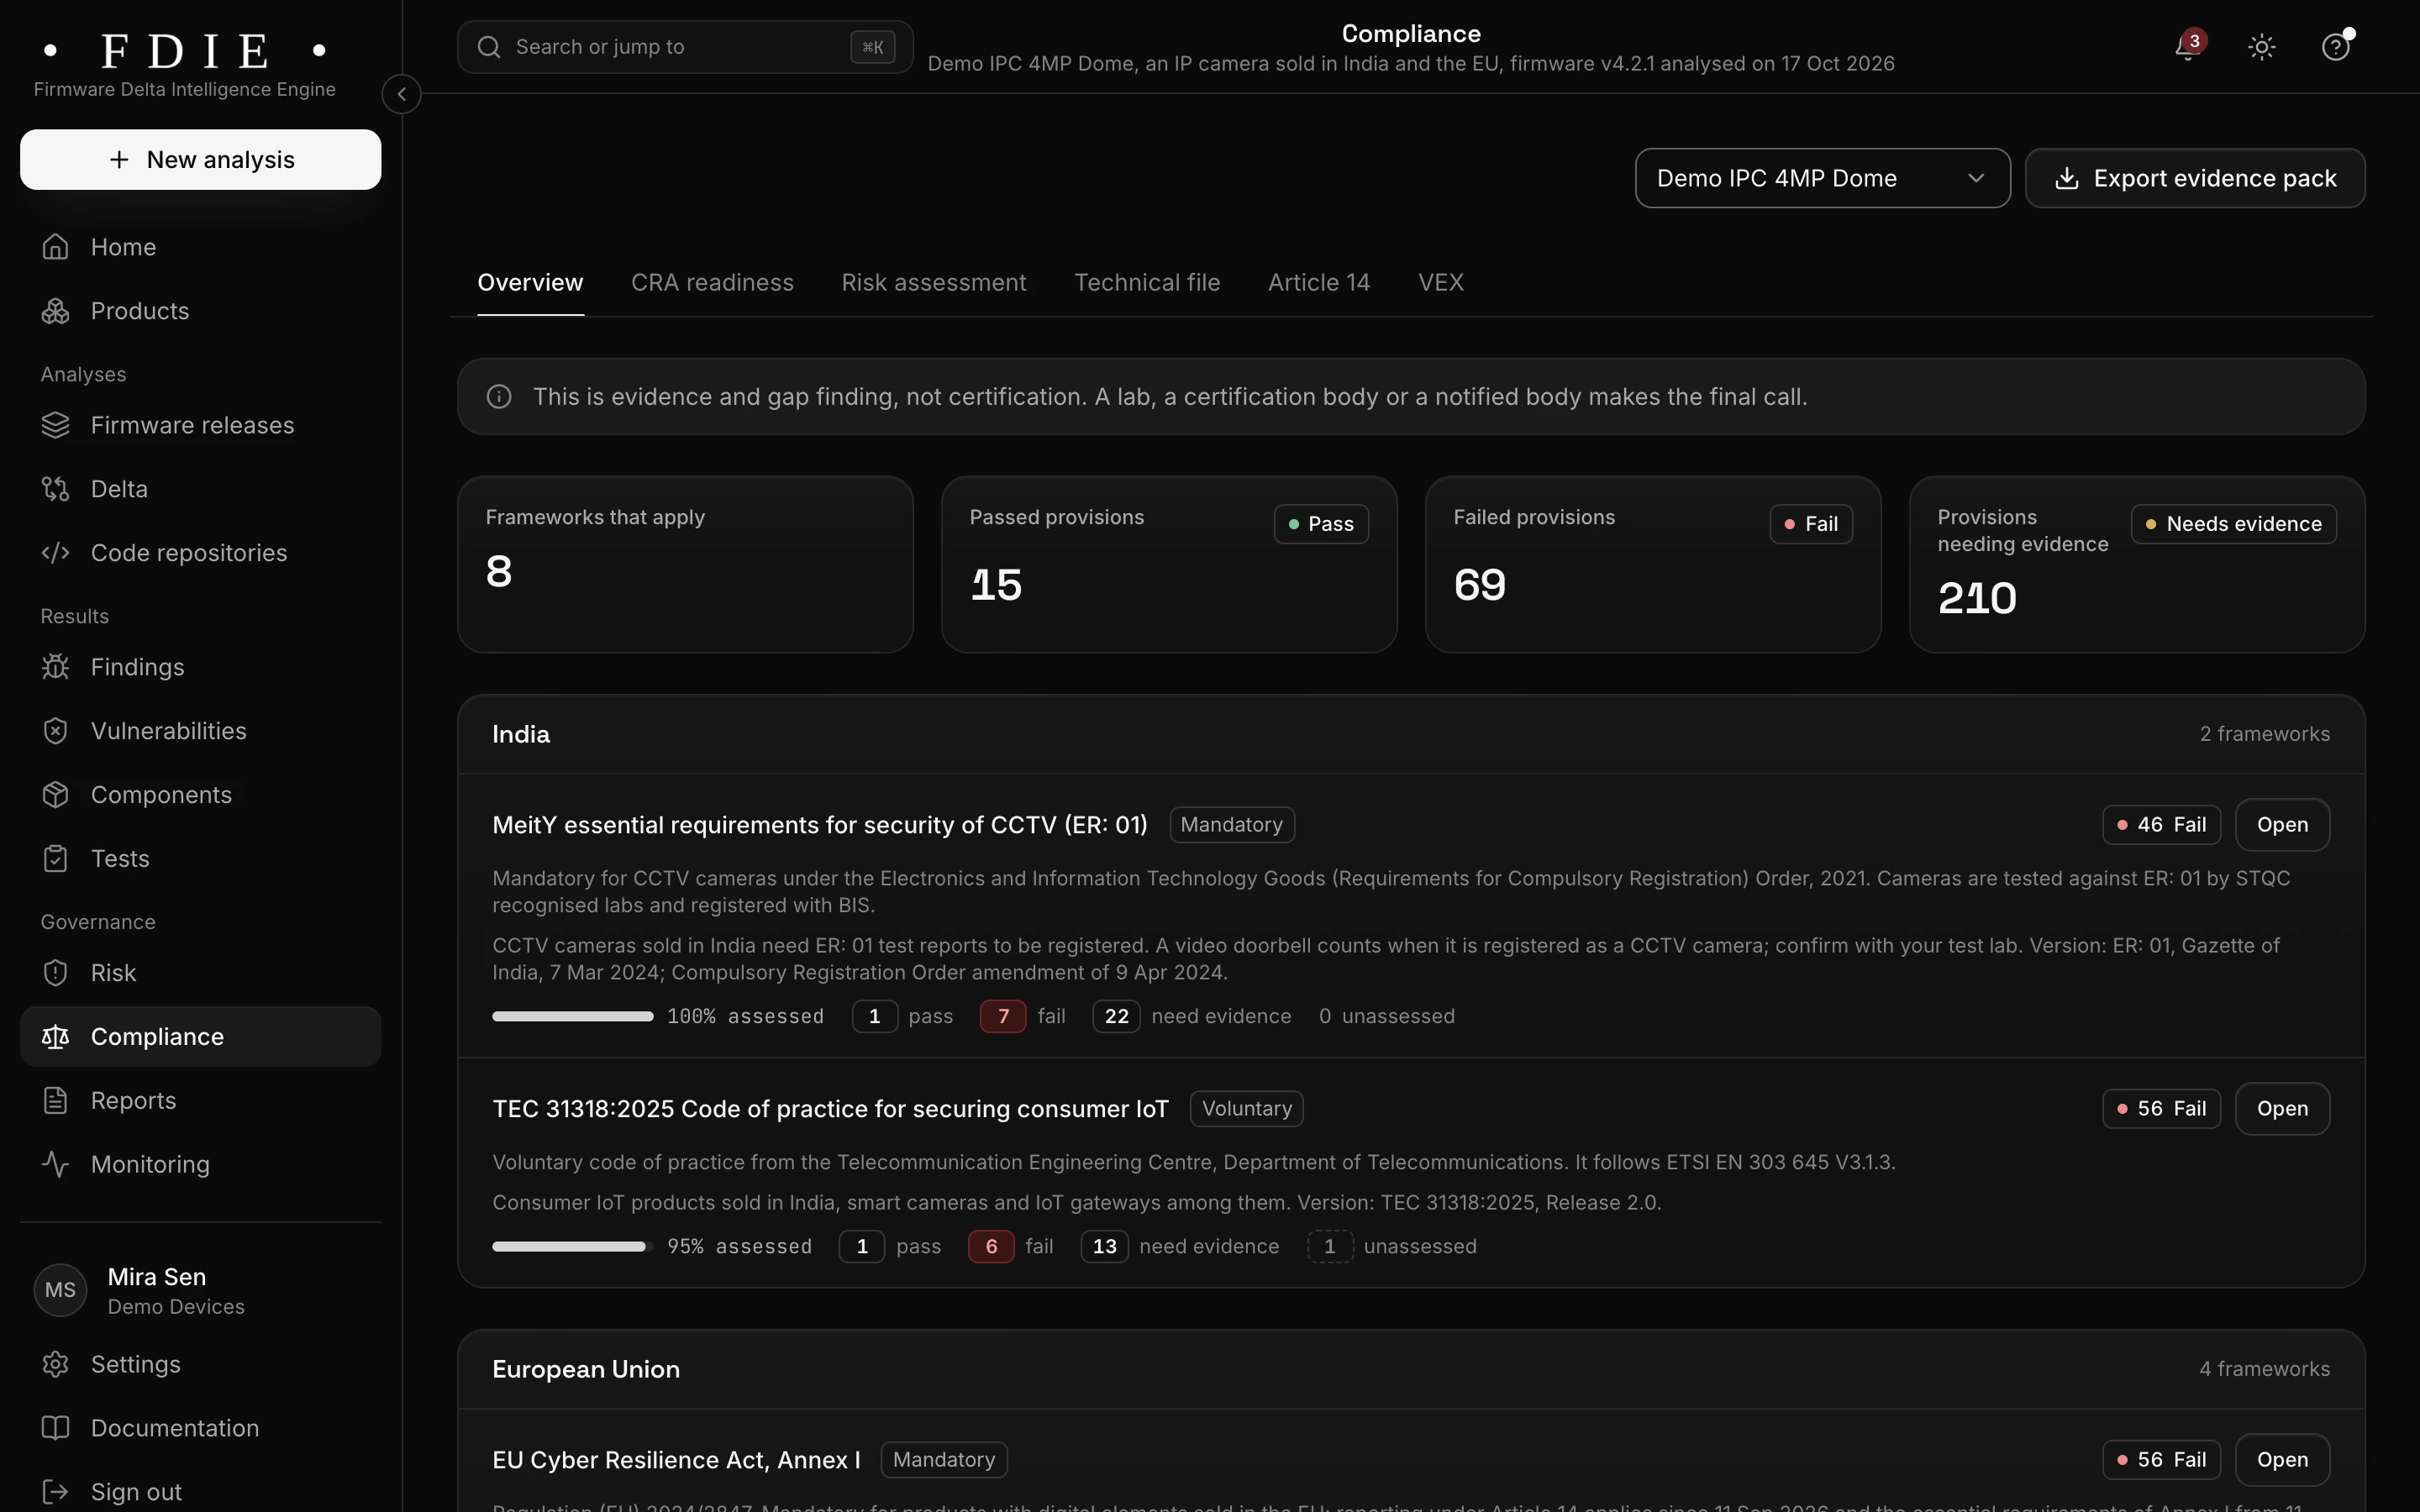
Labs, tenders and buyers ask for proof. Fourteen frameworks across India, the EU, the US and international standards: each requirement shows what passed, what failed and what still needs your evidence. A test lab or certification body makes the final call.
Which rules apply where you sell
Each market asks for different proof. Every provision is assessed for each analysed release of a product the framework applies to.
India
- TEC 31318:2025Voluntary
- MeitY ER-01Mandatory
- NCCS ITSAR for IP routersMandatory
- NCCS ITSAR for Wi-Fi CPEMandatory
CCTV cameras, IP routers and Wi-Fi CPE sold in India need certification. TEC 31318 is a voluntary code for consumer IoT.
European Union
- EU Cyber Resilience Act, Annex IMandatory
- EN 18031-1Harmonised
- EN 18031-2Harmonised
- EN 18031-3Harmonised
- prEN 40000 draftsDraft
The CRA covers connected products on the EU market. EN 18031 shows radio equipment meets the Radio Equipment Directive until December 2027.
United States
- NIST IR 8425Voluntary
- NIST IR 8259AVoluntary
Voluntary baselines that buyers, federal procurement and labelling programmes start from.
International
- ETSI EN 303 645Voluntary
- IEC 62443-4-2Voluntary
- OWASP FSTMTesting method
ETSI EN 303 645 for consumer devices, IEC 62443-4-2 for industrial components such as gateways, and OWASP's firmware testing method.
India
Selling cameras or routers in India
MeitY ER-01
CCTV and IP cameras
- Mandatory for camera models registered with BIS since 9 April 2025, other than analog cameras.
- The device checks decide 4 of its 30 provisions, such as signed updates, and give evidence for 8 more, such as closed serial and USB debug interfaces.
- The lab still tests the camera itself and audits manufacturing.
NCCS ITSAR
IP routers and Wi-Fi CPE
- Security certification under the ComSec scheme of MTCTE, mandatory for new models since 1 July 2024.
- In the app as two frameworks, version 2.0.0: 179 provisions for IP routers and 133 for Wi-Fi CPE.
- The device checks decide 5 of the 312 and give evidence for 73 more; the lab runs the rest on the device.
European Union
Exporting to the EU: the Cyber Resilience Act
Selling into the EU means a technical file for each product and reports within hours of an actively exploited flaw. The app keeps the CRA technical file for each release: the Annex VII documentation, the EU declaration of conformity and the user information, filled in from the analysis and completed by your team. The Article 13 risk assessment is prefilled from the newest analysed release and signed off by an owner other than the person asking.
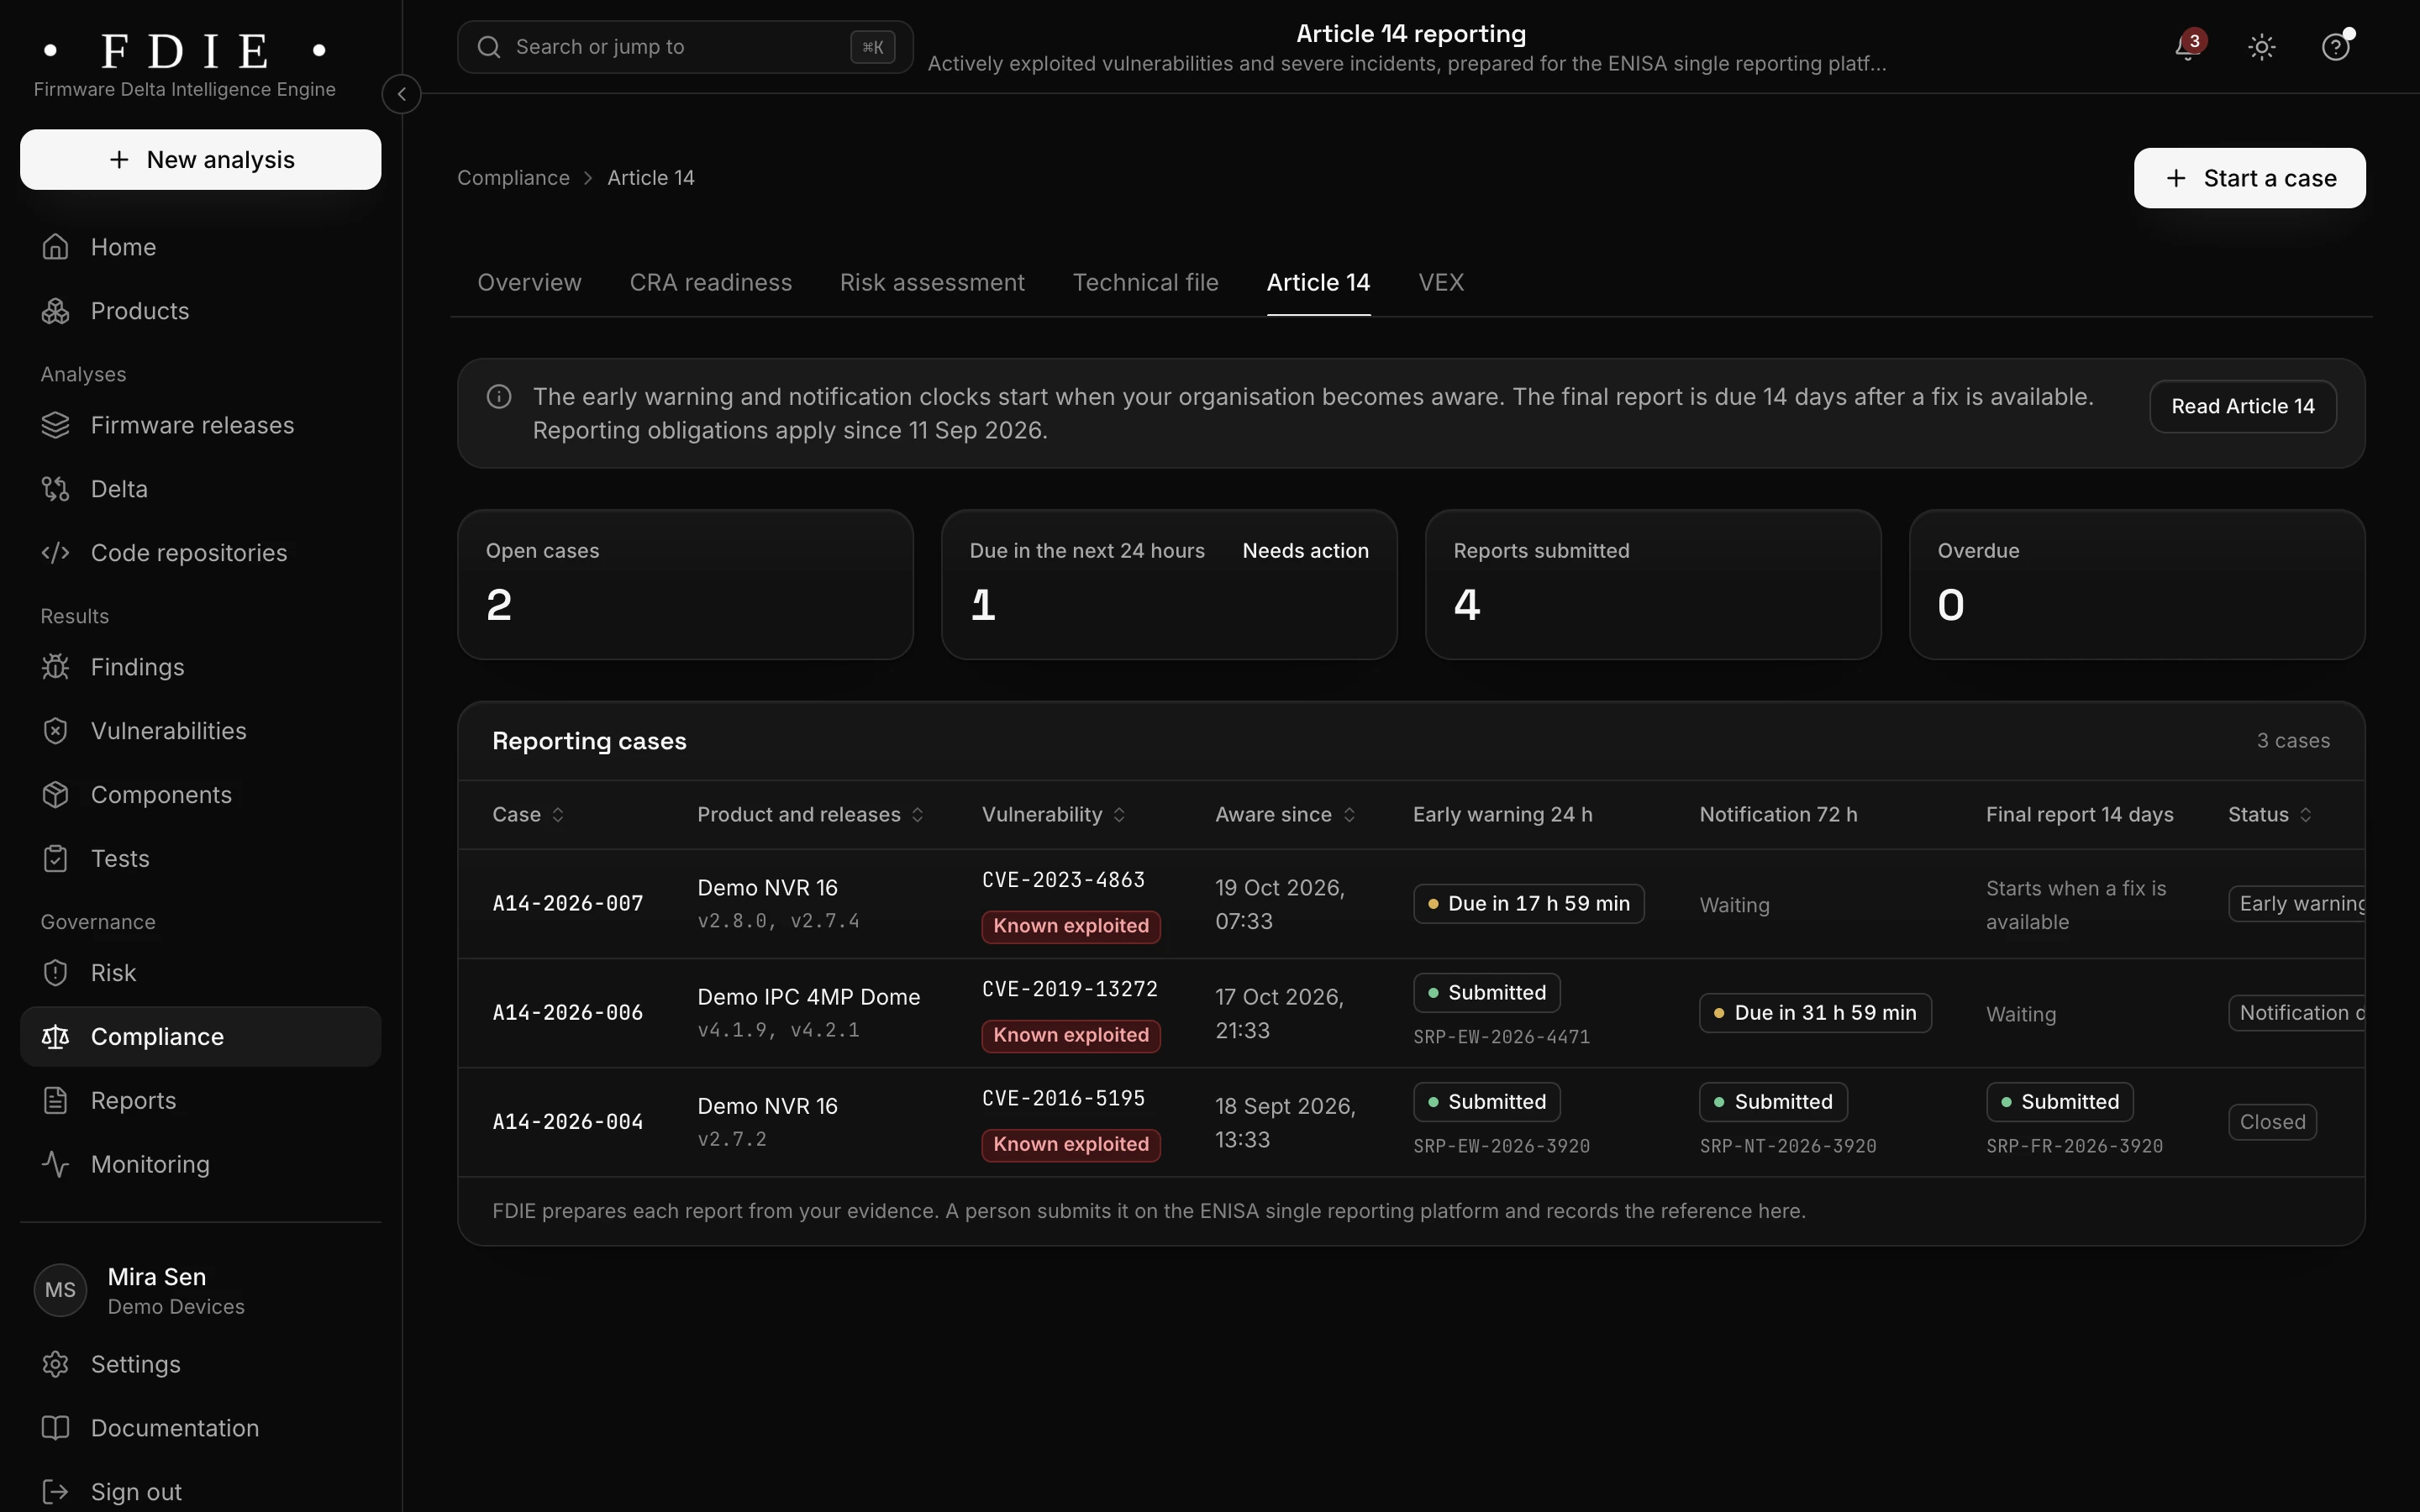
Article 14 reporting, since 11 September 2026
Aware
You record when you learnt of an actively exploited vulnerability
24 hours
Early warning
72 hours
Vulnerability notification
14 days after a fix
Final report
The app runs the clocks, reminds you 24 hours before each report is due and prefills it from your evidence; a person submits it on ENISA's platform. The CRA's other requirements apply from 11 December 2027.
Answer buyers and labs in their own format
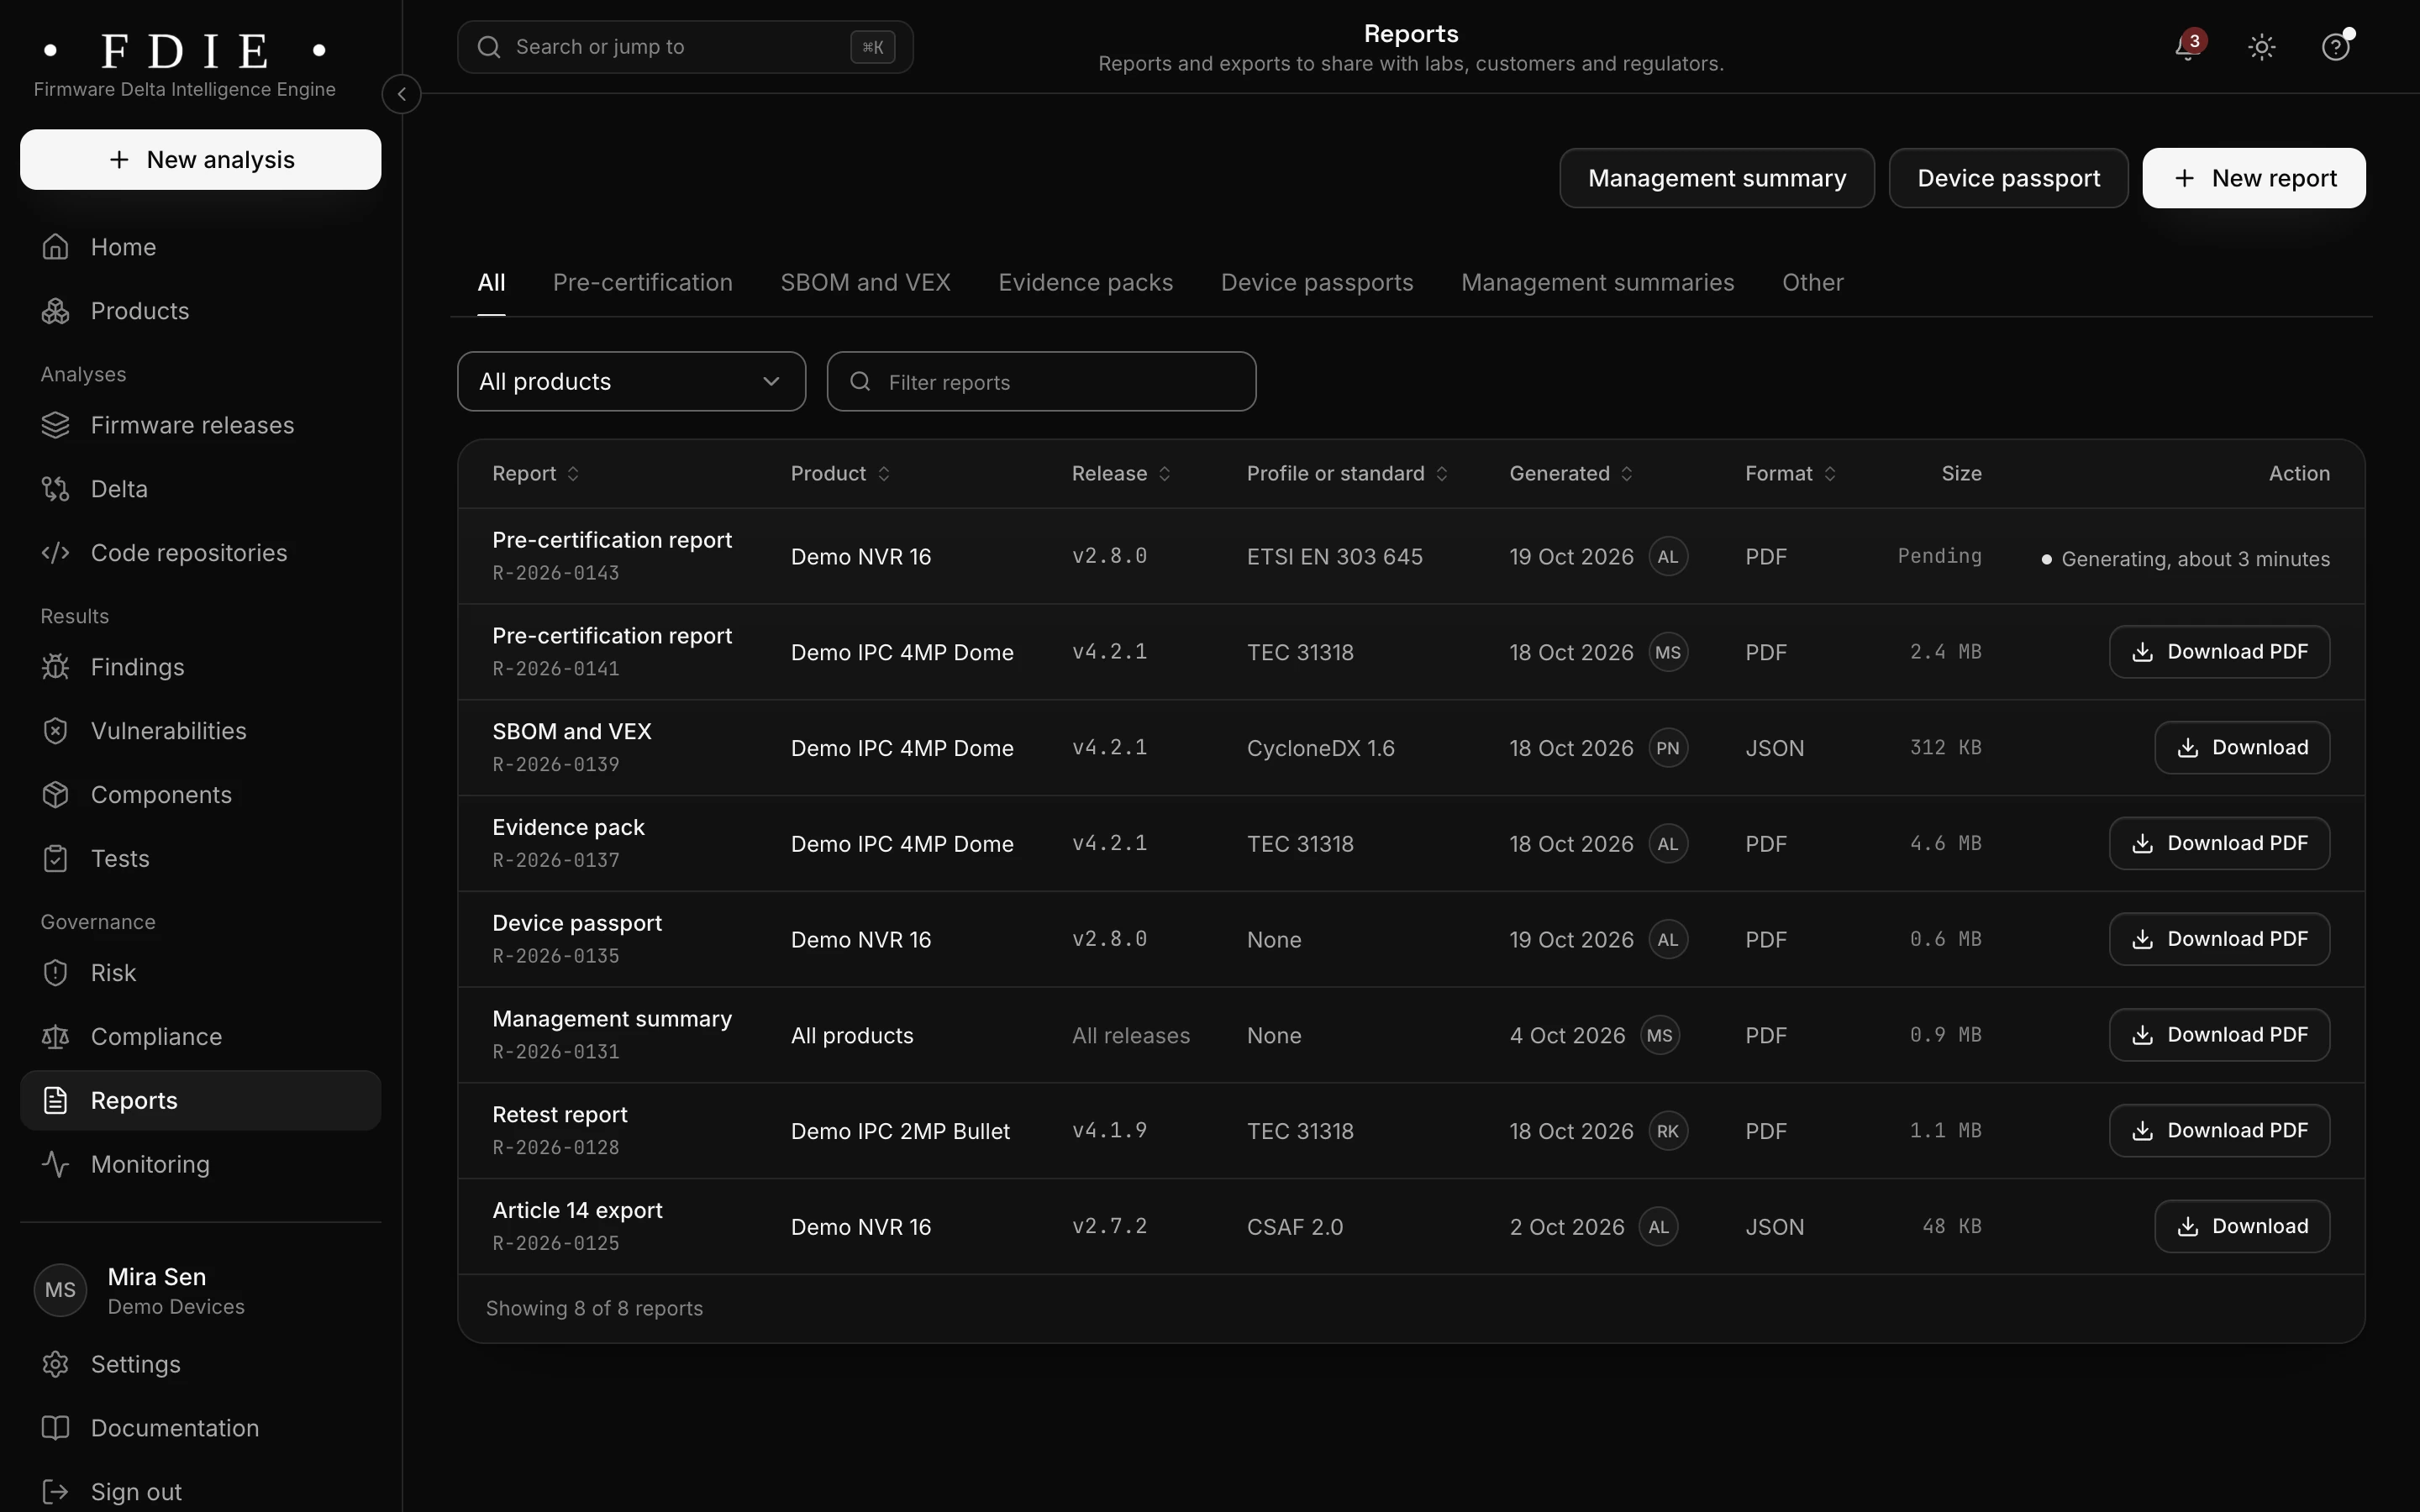
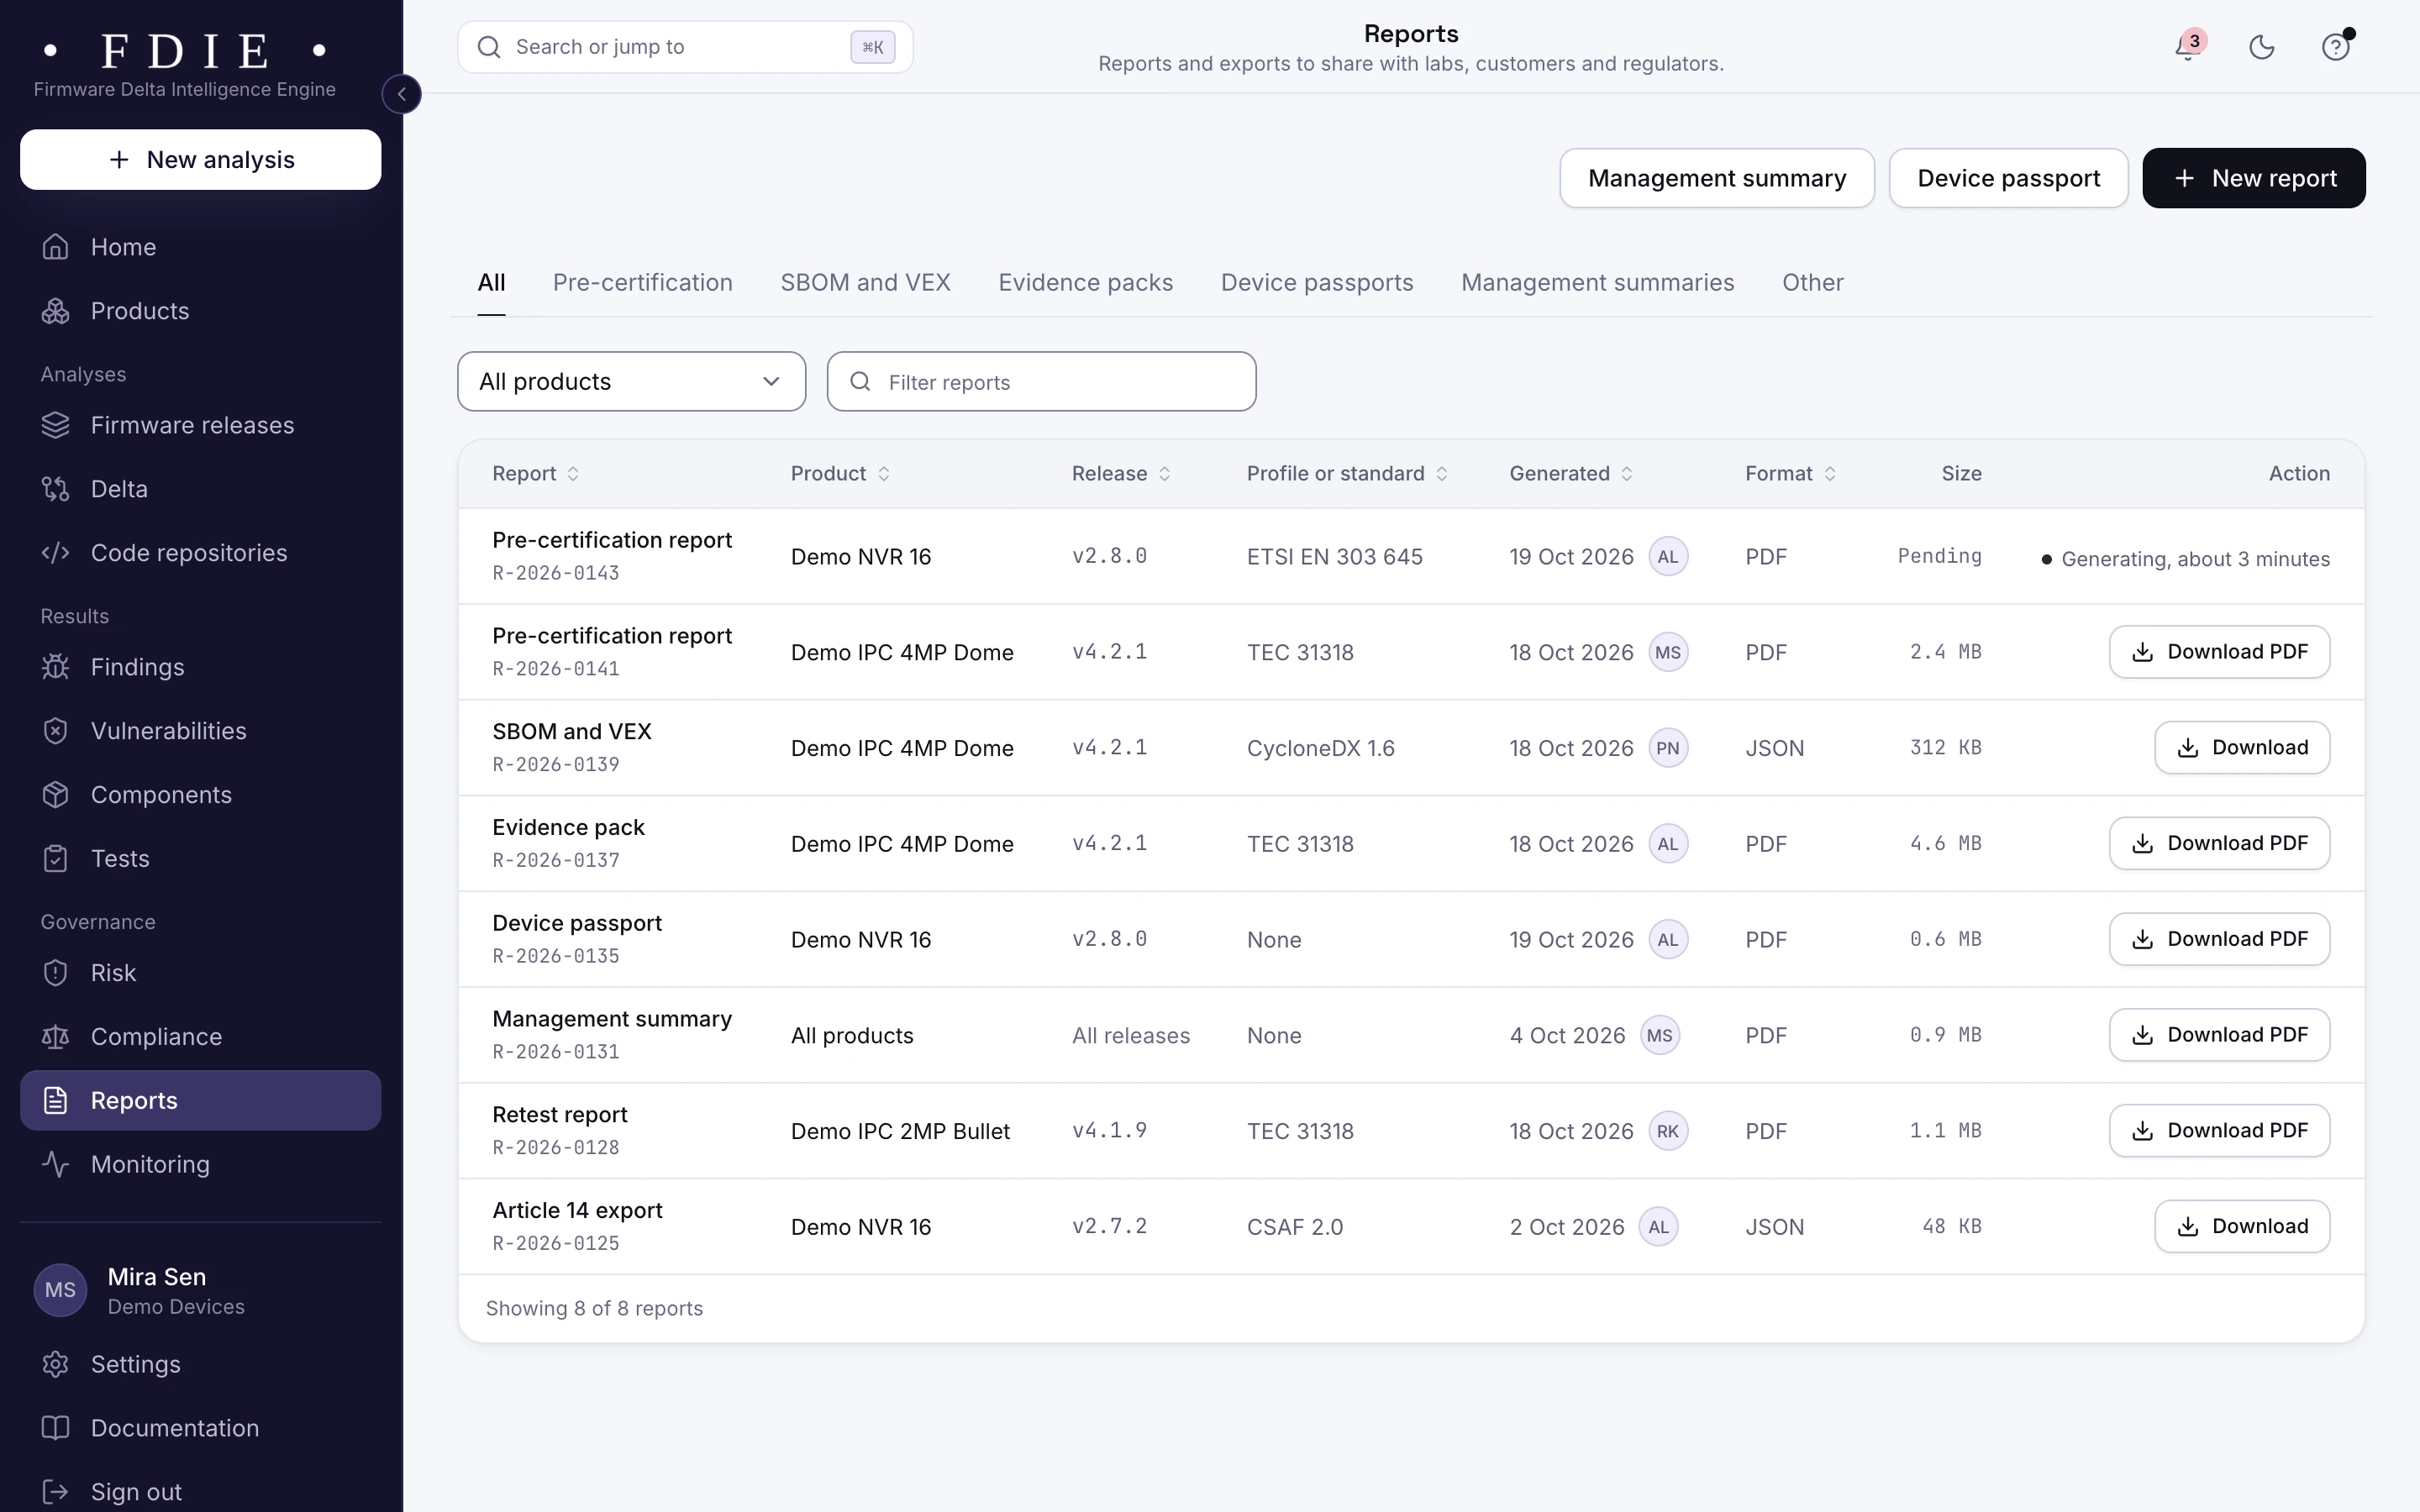
Your team records whether each vulnerability affects the product, as VEX in CycloneDX, OpenVEX or CSAF 2.0. Reports are signed PDFs built from the analysis: pre-certification reports against TEC 31318, ETSI EN 303 645 or the CRA, evidence packs, device passports, retest and delta reports, and the CRA documents.
Why a pass here means something
Nothing passes without one of these.
Device checks
The 64 checks of the product's newest analysed release
Findings and product data
Firmware and code findings, and what the product declares, such as its disclosure policy and support period
Your evidence
Documents, test reports and procedures your team adds
Sign-off
The Article 13 risk assessment, signed off by an owner
Questions
Which frameworks are in the app?
Fourteen. For India: MeitY ER-01, NCCS ITSAR for IP routers and for Wi-Fi CPE, and TEC 31318. For the EU: the Cyber Resilience Act Annex I, EN 18031-1, -2 and -3, and the prEN 40000 drafts. For the US: NIST IR 8425 and NIST IR 8259A. Internationally: ETSI EN 303 645, IEC 62443-4-2 and OWASP FSTM as a testing method.
Does the app submit Article 14 reports for us?
No. A person in your organisation submits each report on ENISA's single reporting platform. The app keeps the clocks, prefills each report from your evidence and records the reference you receive.
Can we give the evidence to our lab?
Yes. The evidence pack lists the evidence for each provision of the chosen framework, with who added it and when, and the pre-certification report adds the device checks, the fix list and an SBOM and VEX summary.
Do you need our source code?
No. The analysis works on the firmware image. Connecting the source adds findings in your own code to the same product.
Find out what the lab would flag in your firmware
A 45-minute call with our team. Bring one firmware image.