For makers of IP cameras, NVRs, routers, gateways and doorbells
Find firmware security problems before the test lab
The problems that fail cameras and routers at the test lab often sit in code you never wrote: an old OpenSSL, telnet left on, a default password in the chip vendor's SDK. See each one in your firmware before you submit.
- See what the chip vendor's SDK put in your firmware
- Answer "are we affected?" when a flaw makes the news
- Prove each update fixed what it promised
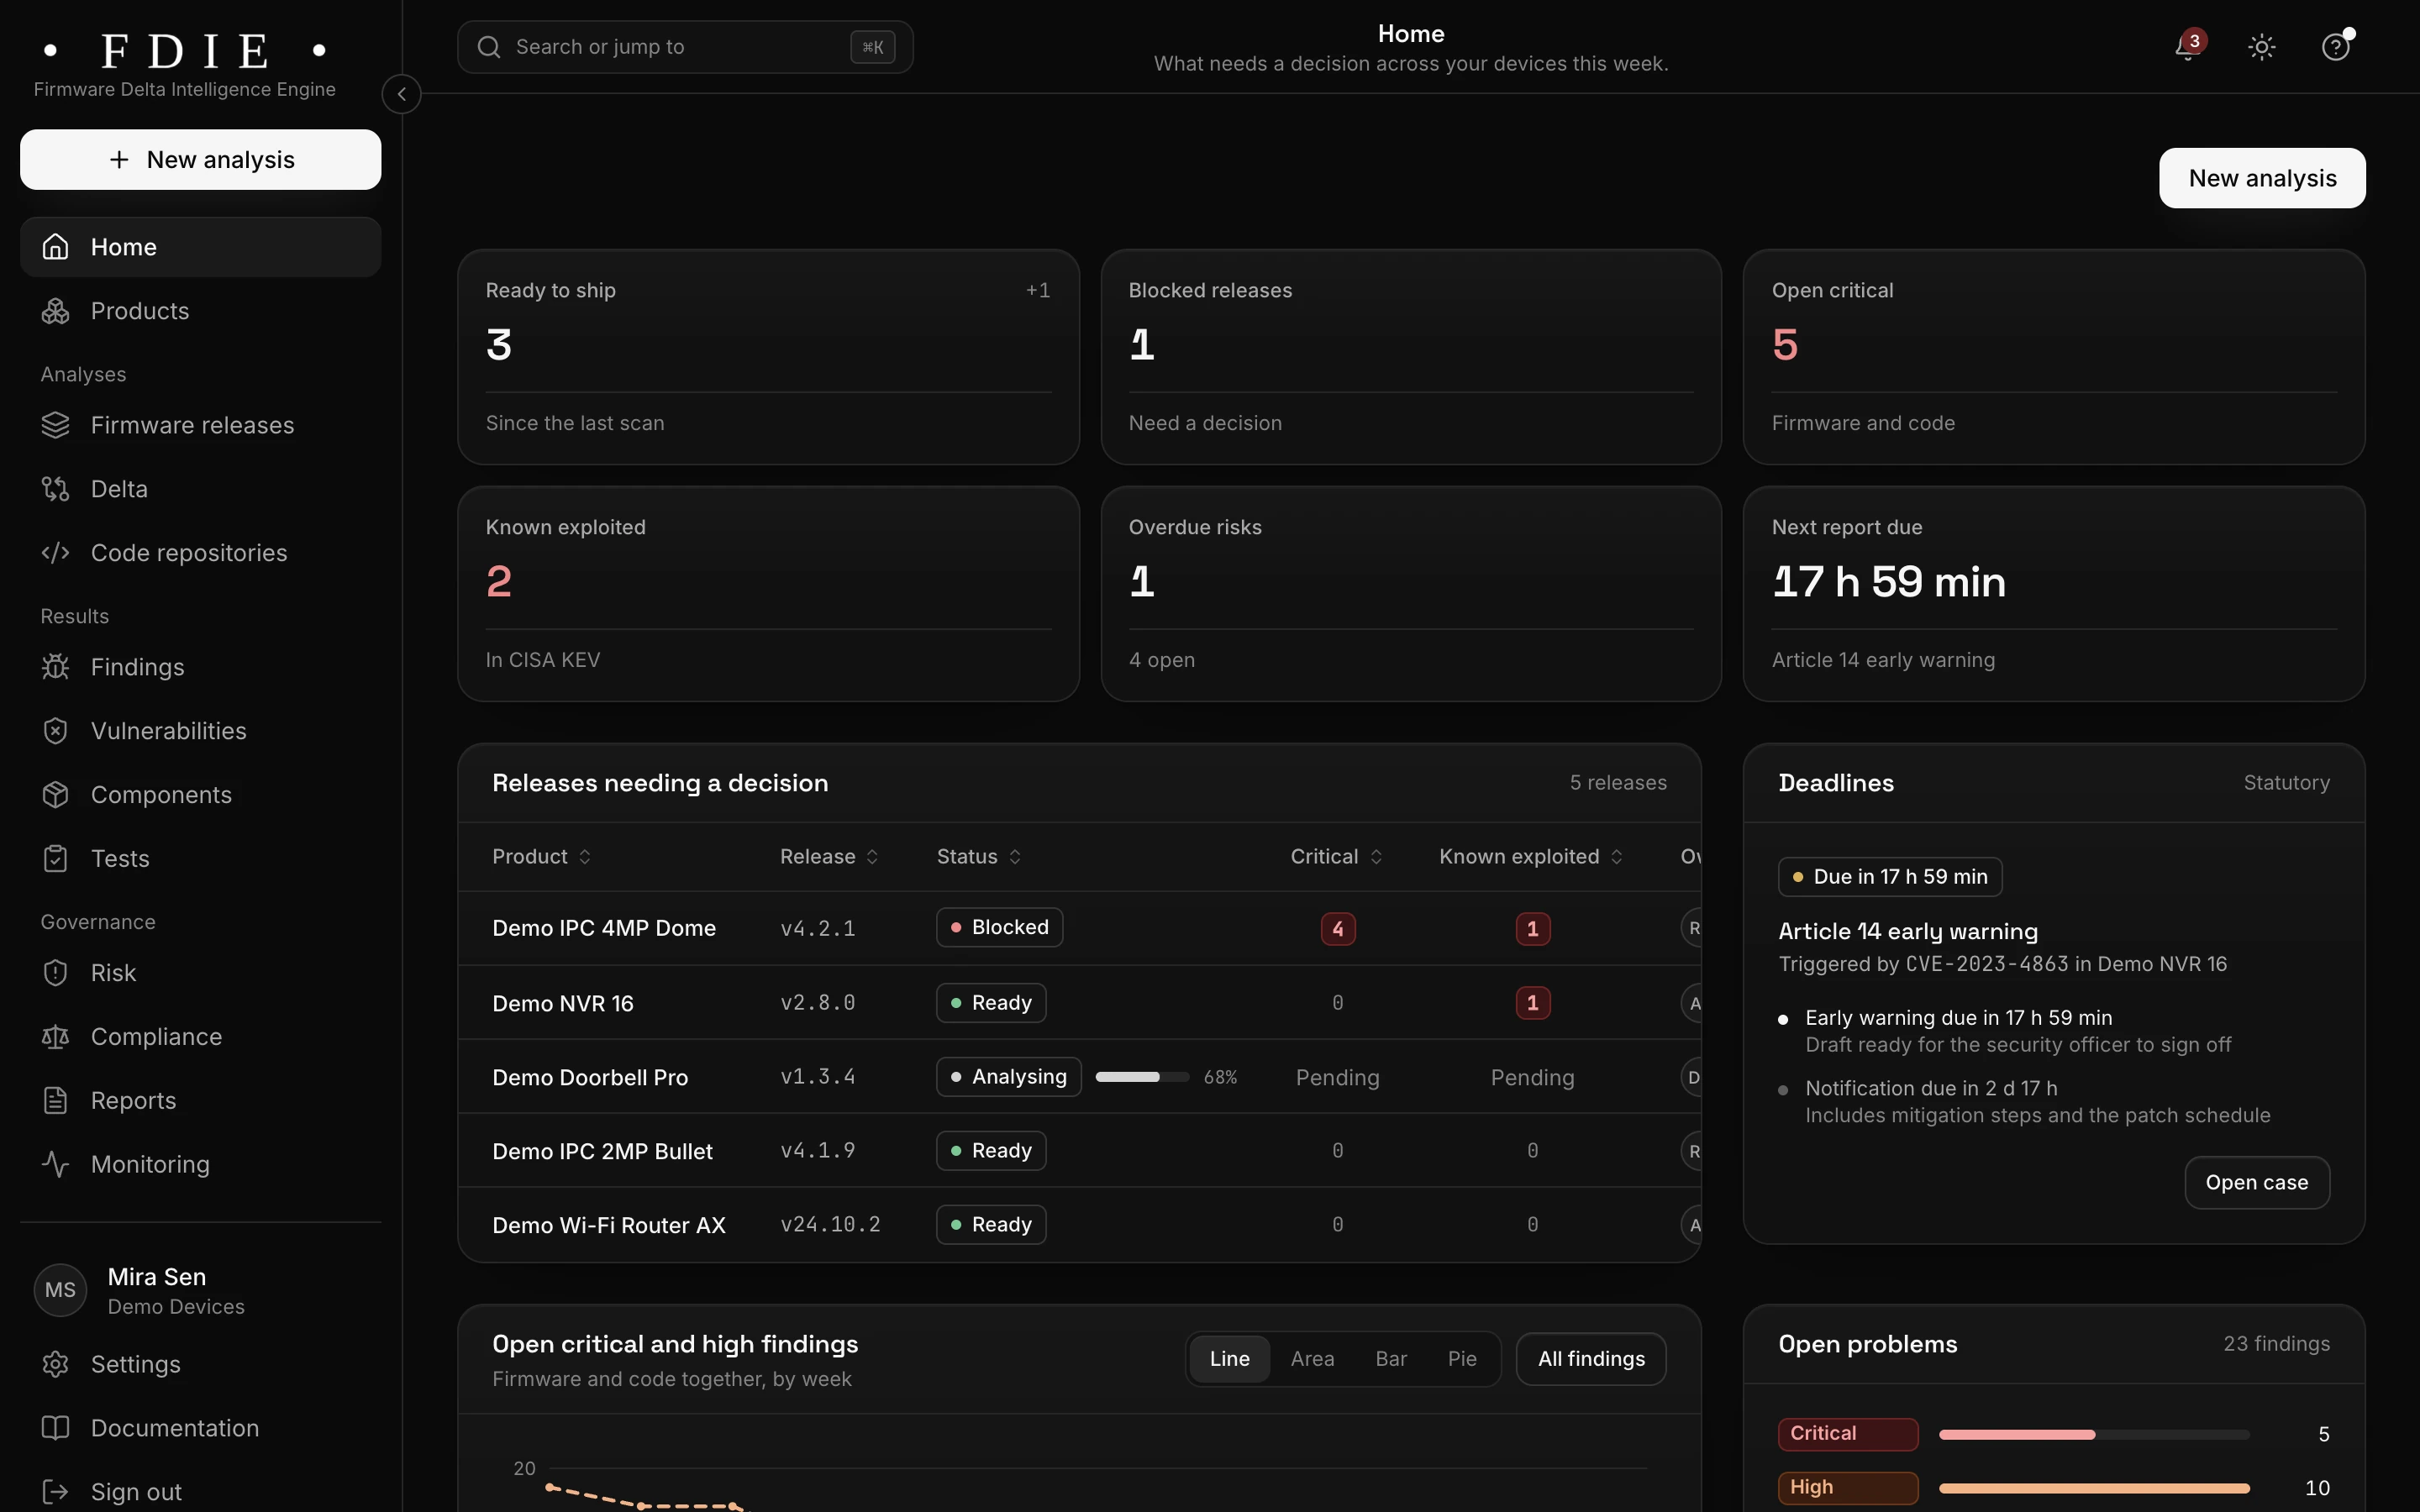
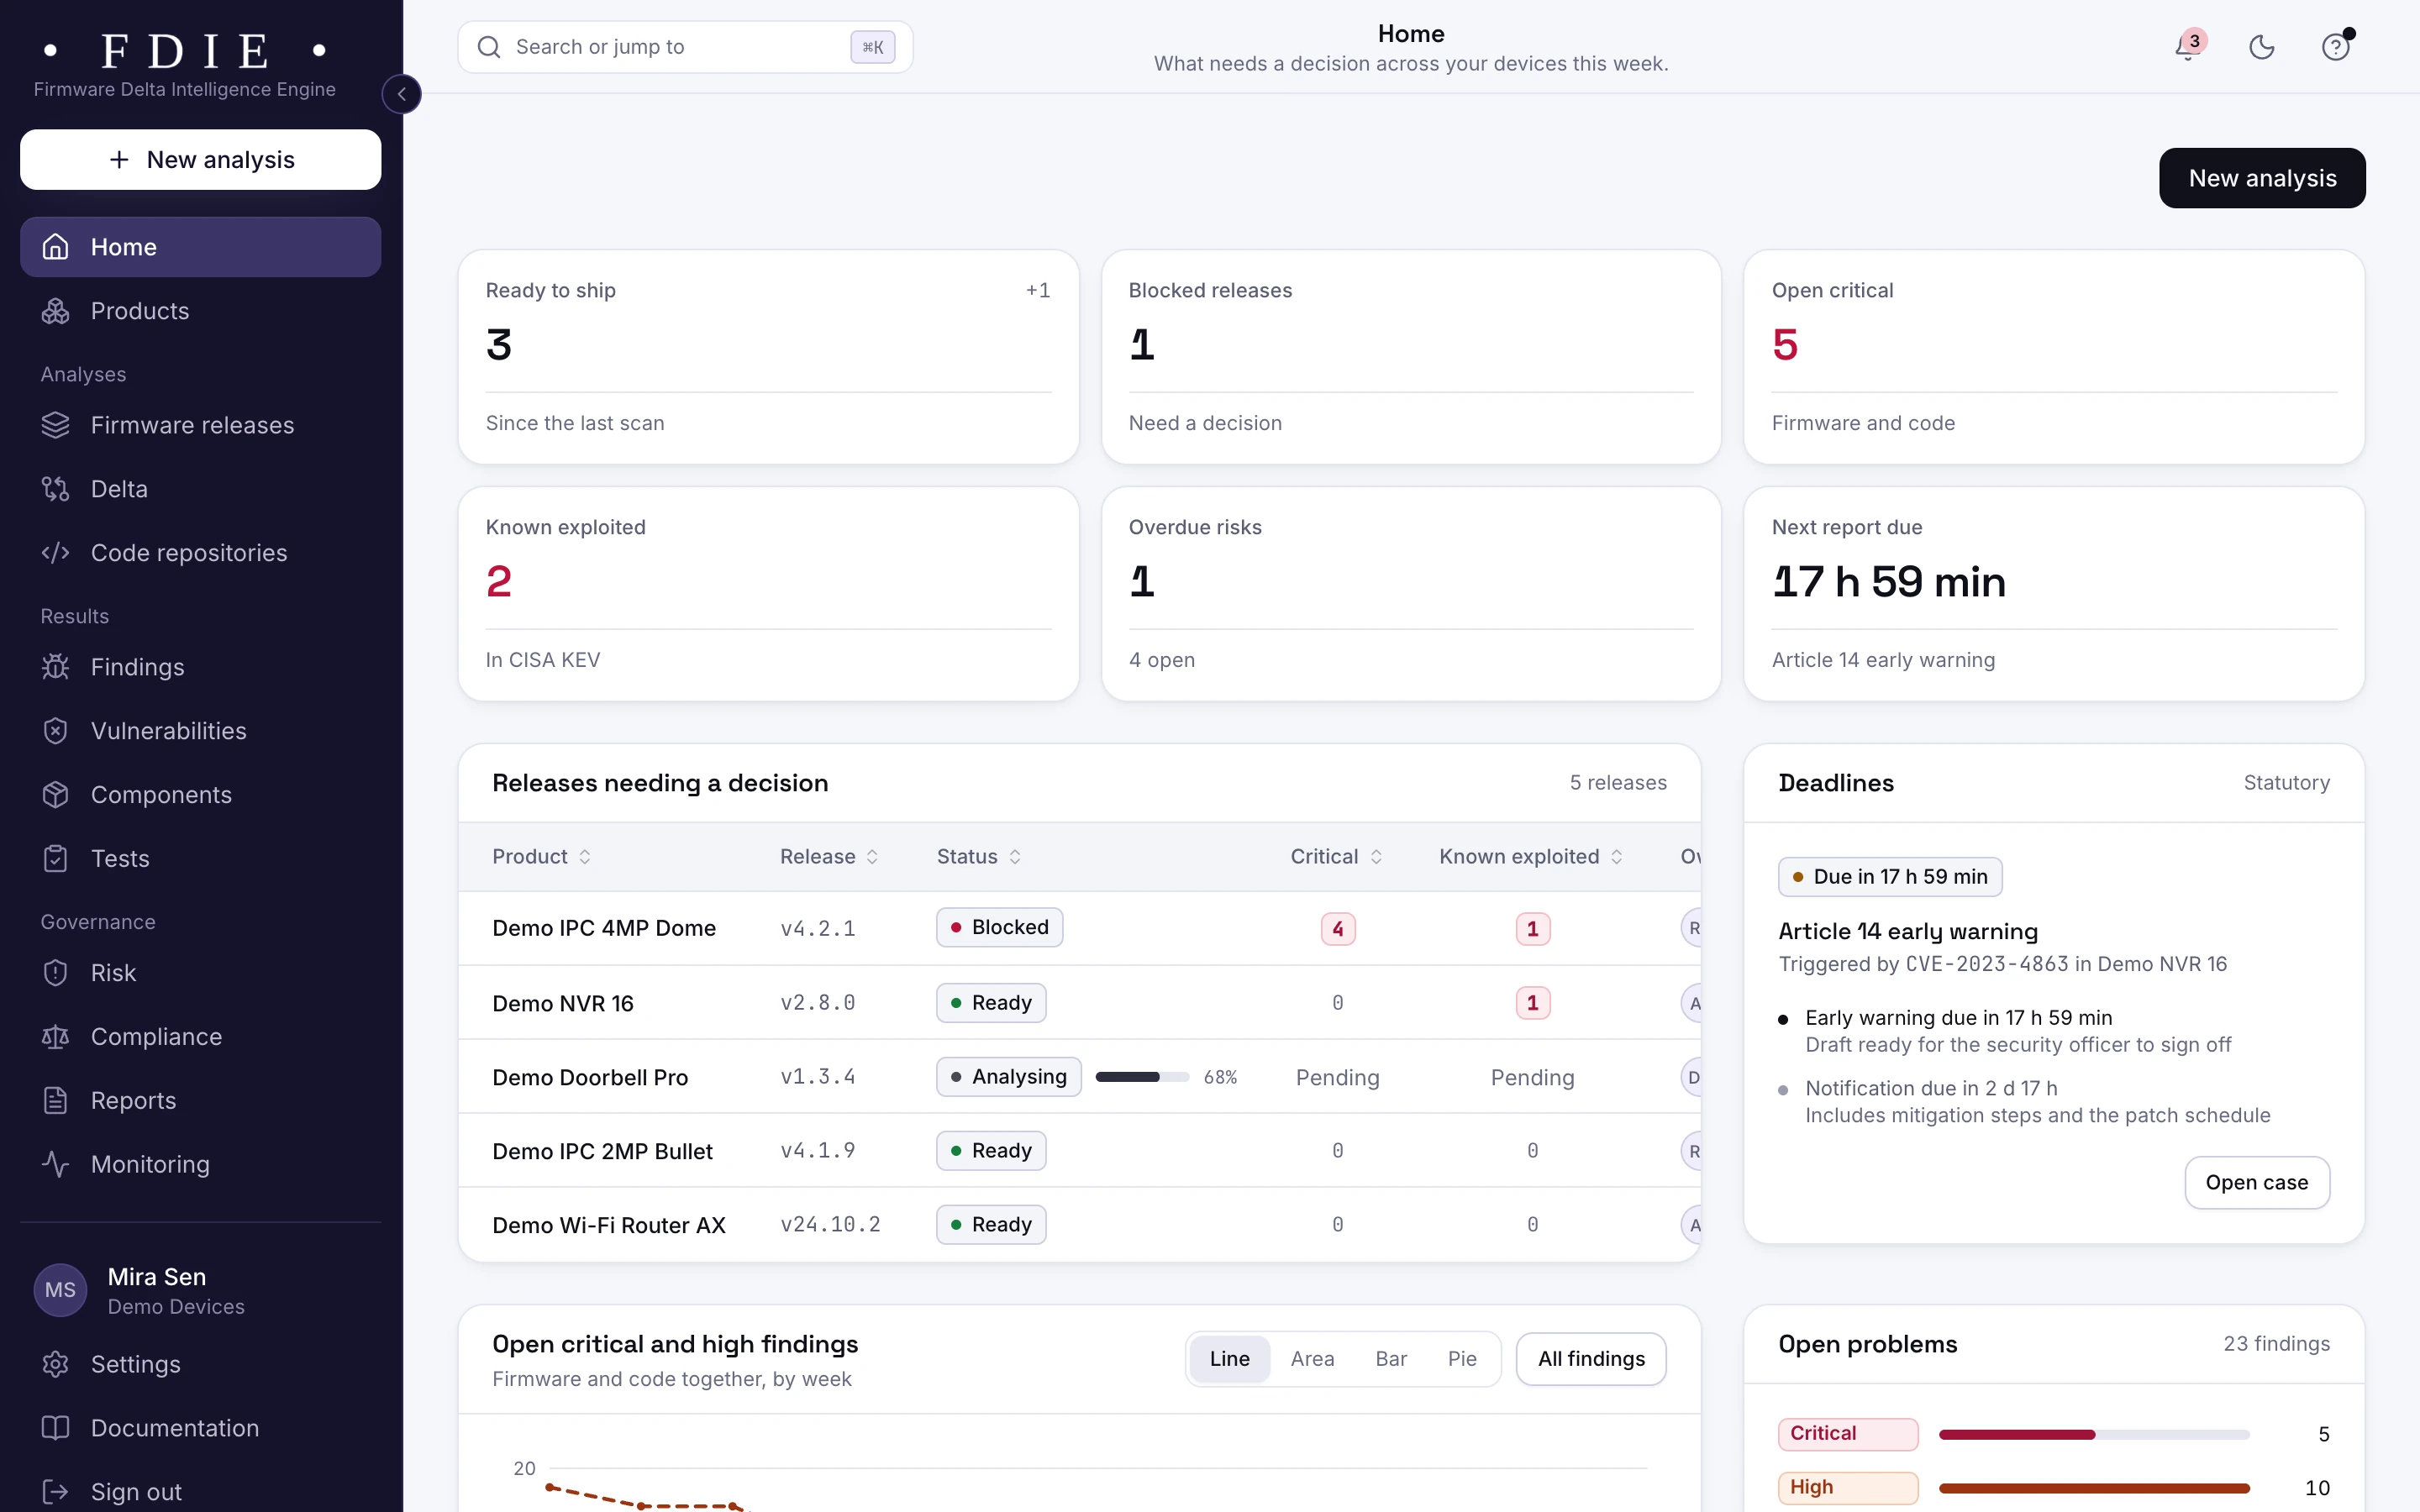
In numbers
- frameworks for India, the EU, the US and international standards
- 14
- device checks in 9 groups
- 64
- code rules, firmware source first
- 1,774
- instruction sets disassembled
- 22
Vulnerability data from NVD, OSV, the CISA Known Exploited Vulnerabilities catalogue and FIRST EPSS.
How it works
Upload the firmware you plan to ship
An image of up to 8 GiB, or imported from GitHub or GitLab. Connect its source code if you have it; you do not need it.
We read everything inside it
Our own readers unpack the image and disassemble its programs; the code engine scans the source. Nothing in the image is run.
Fix what would fail, then ship
A ship or hold decision with its reasons, findings with owners, and reports for your lab, your buyers and tenders.
Before the lab, the tender and the news
Screens from the app, shown with its sample organisation.
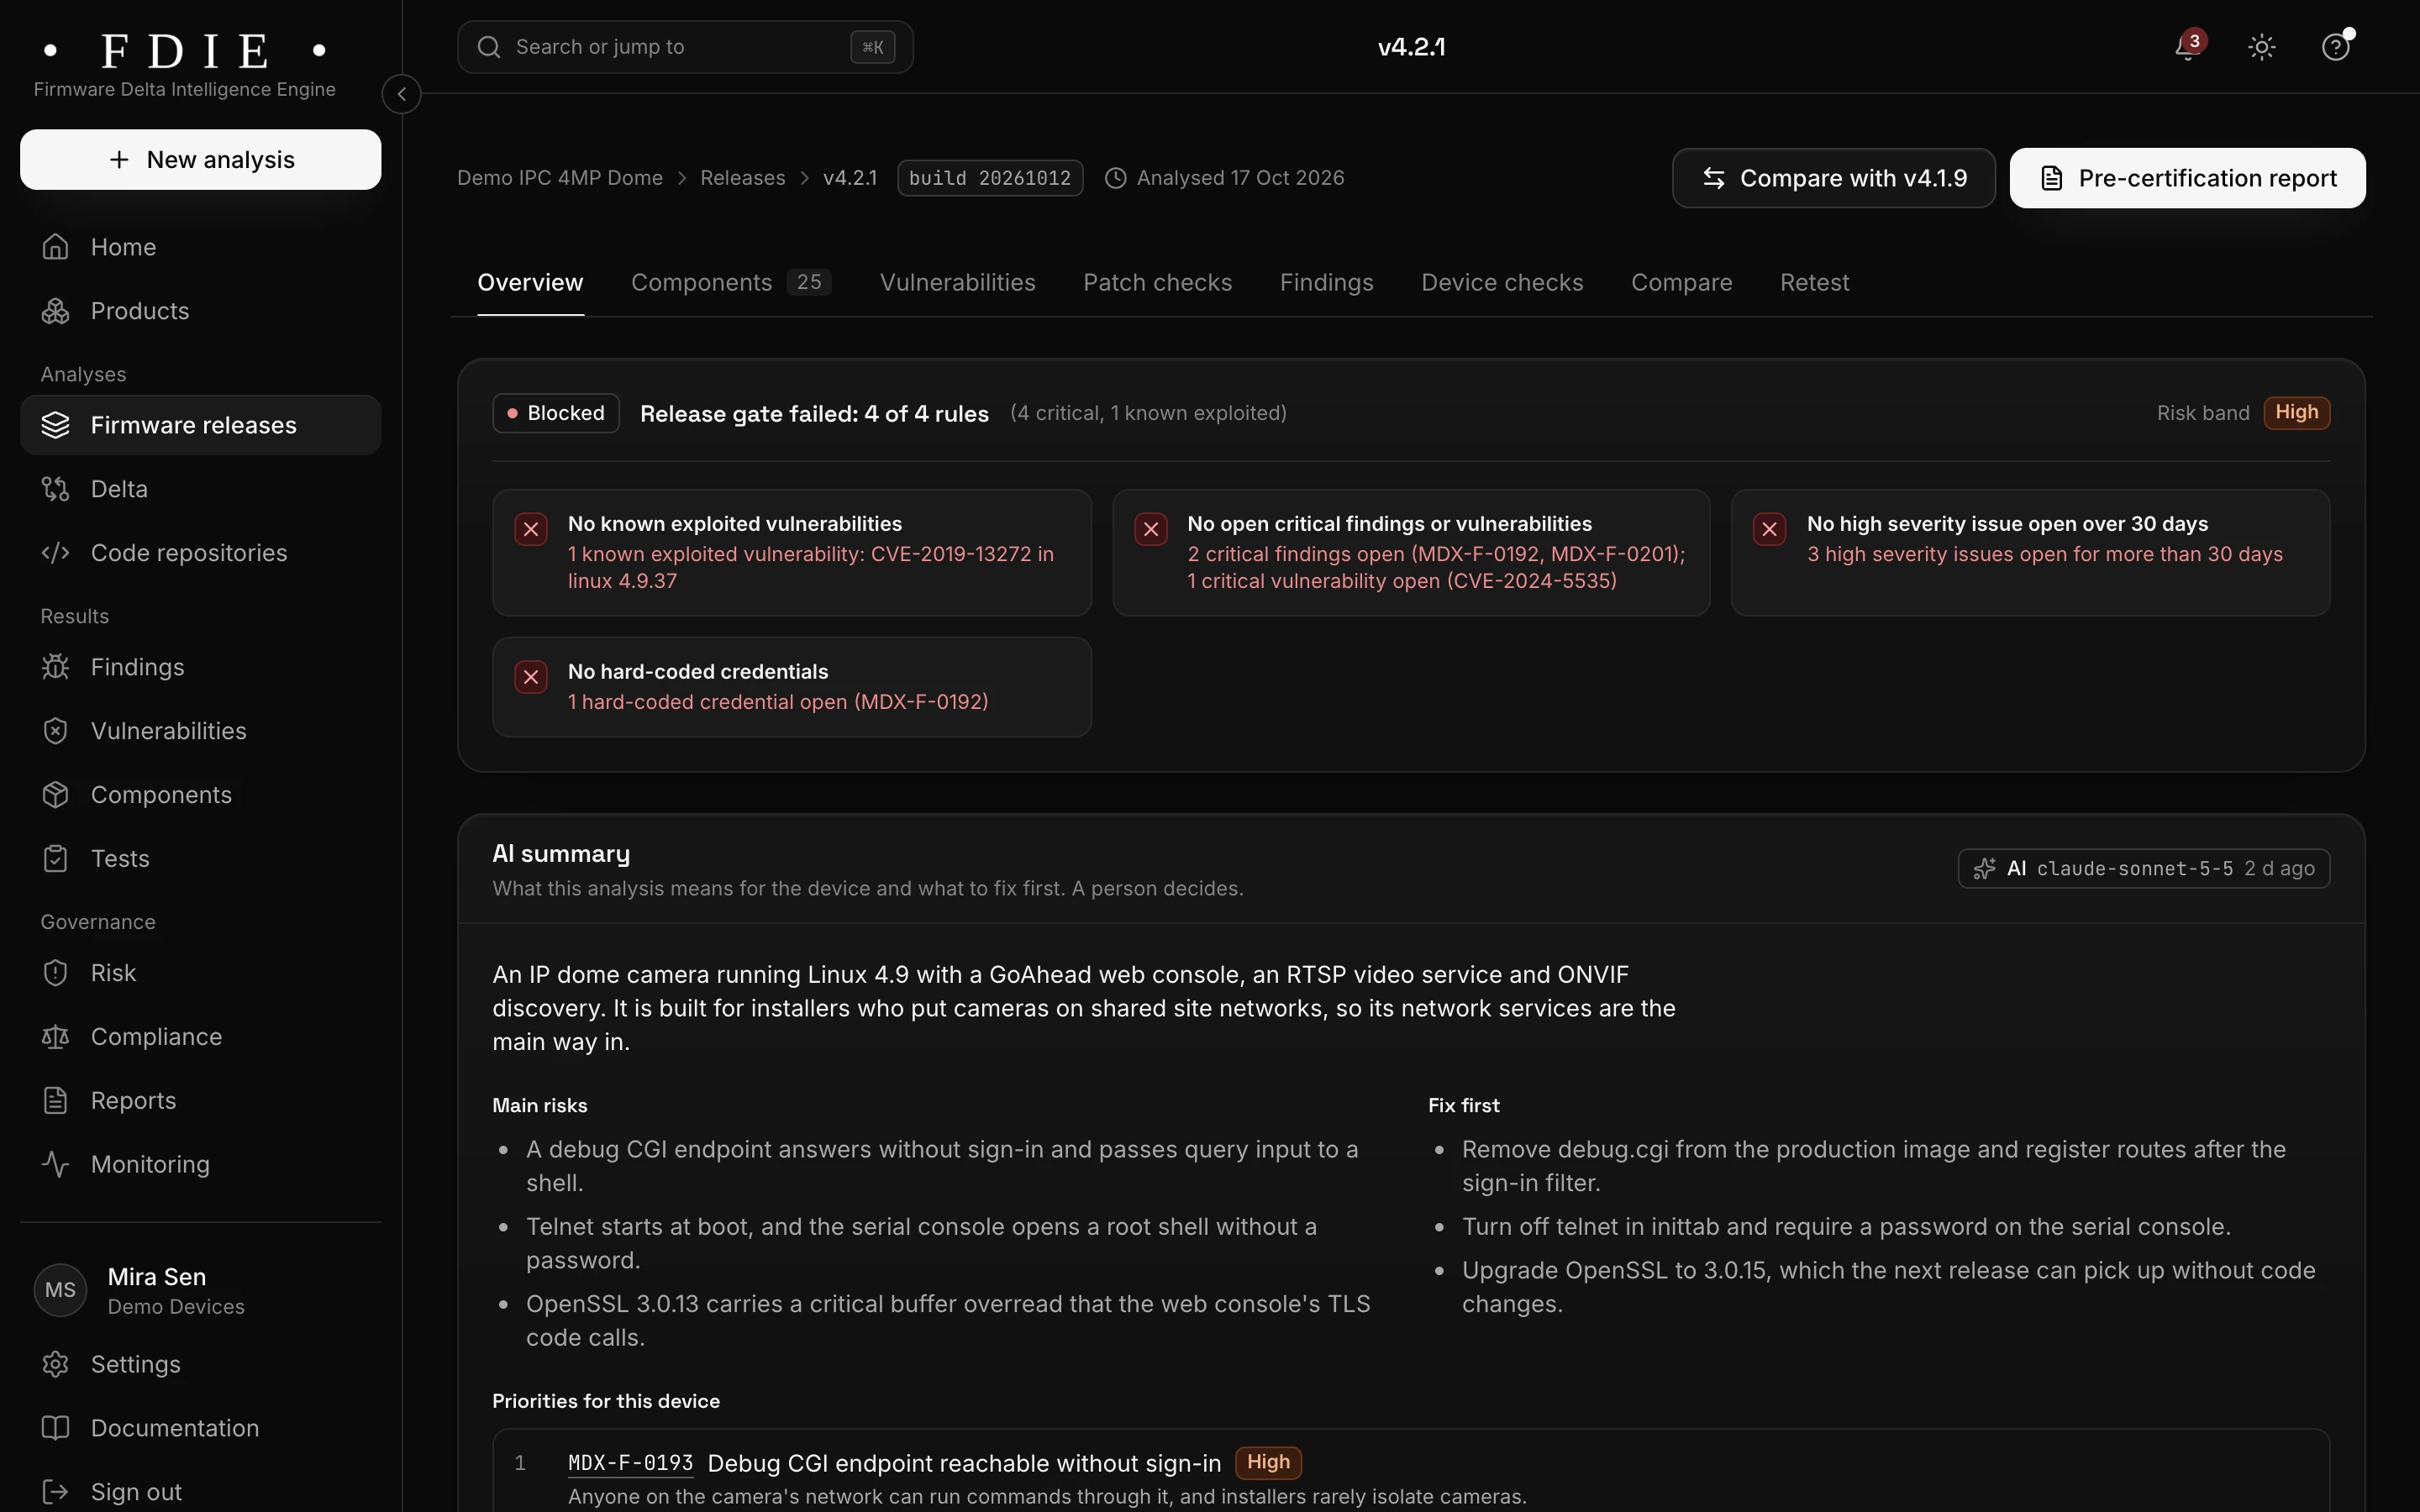
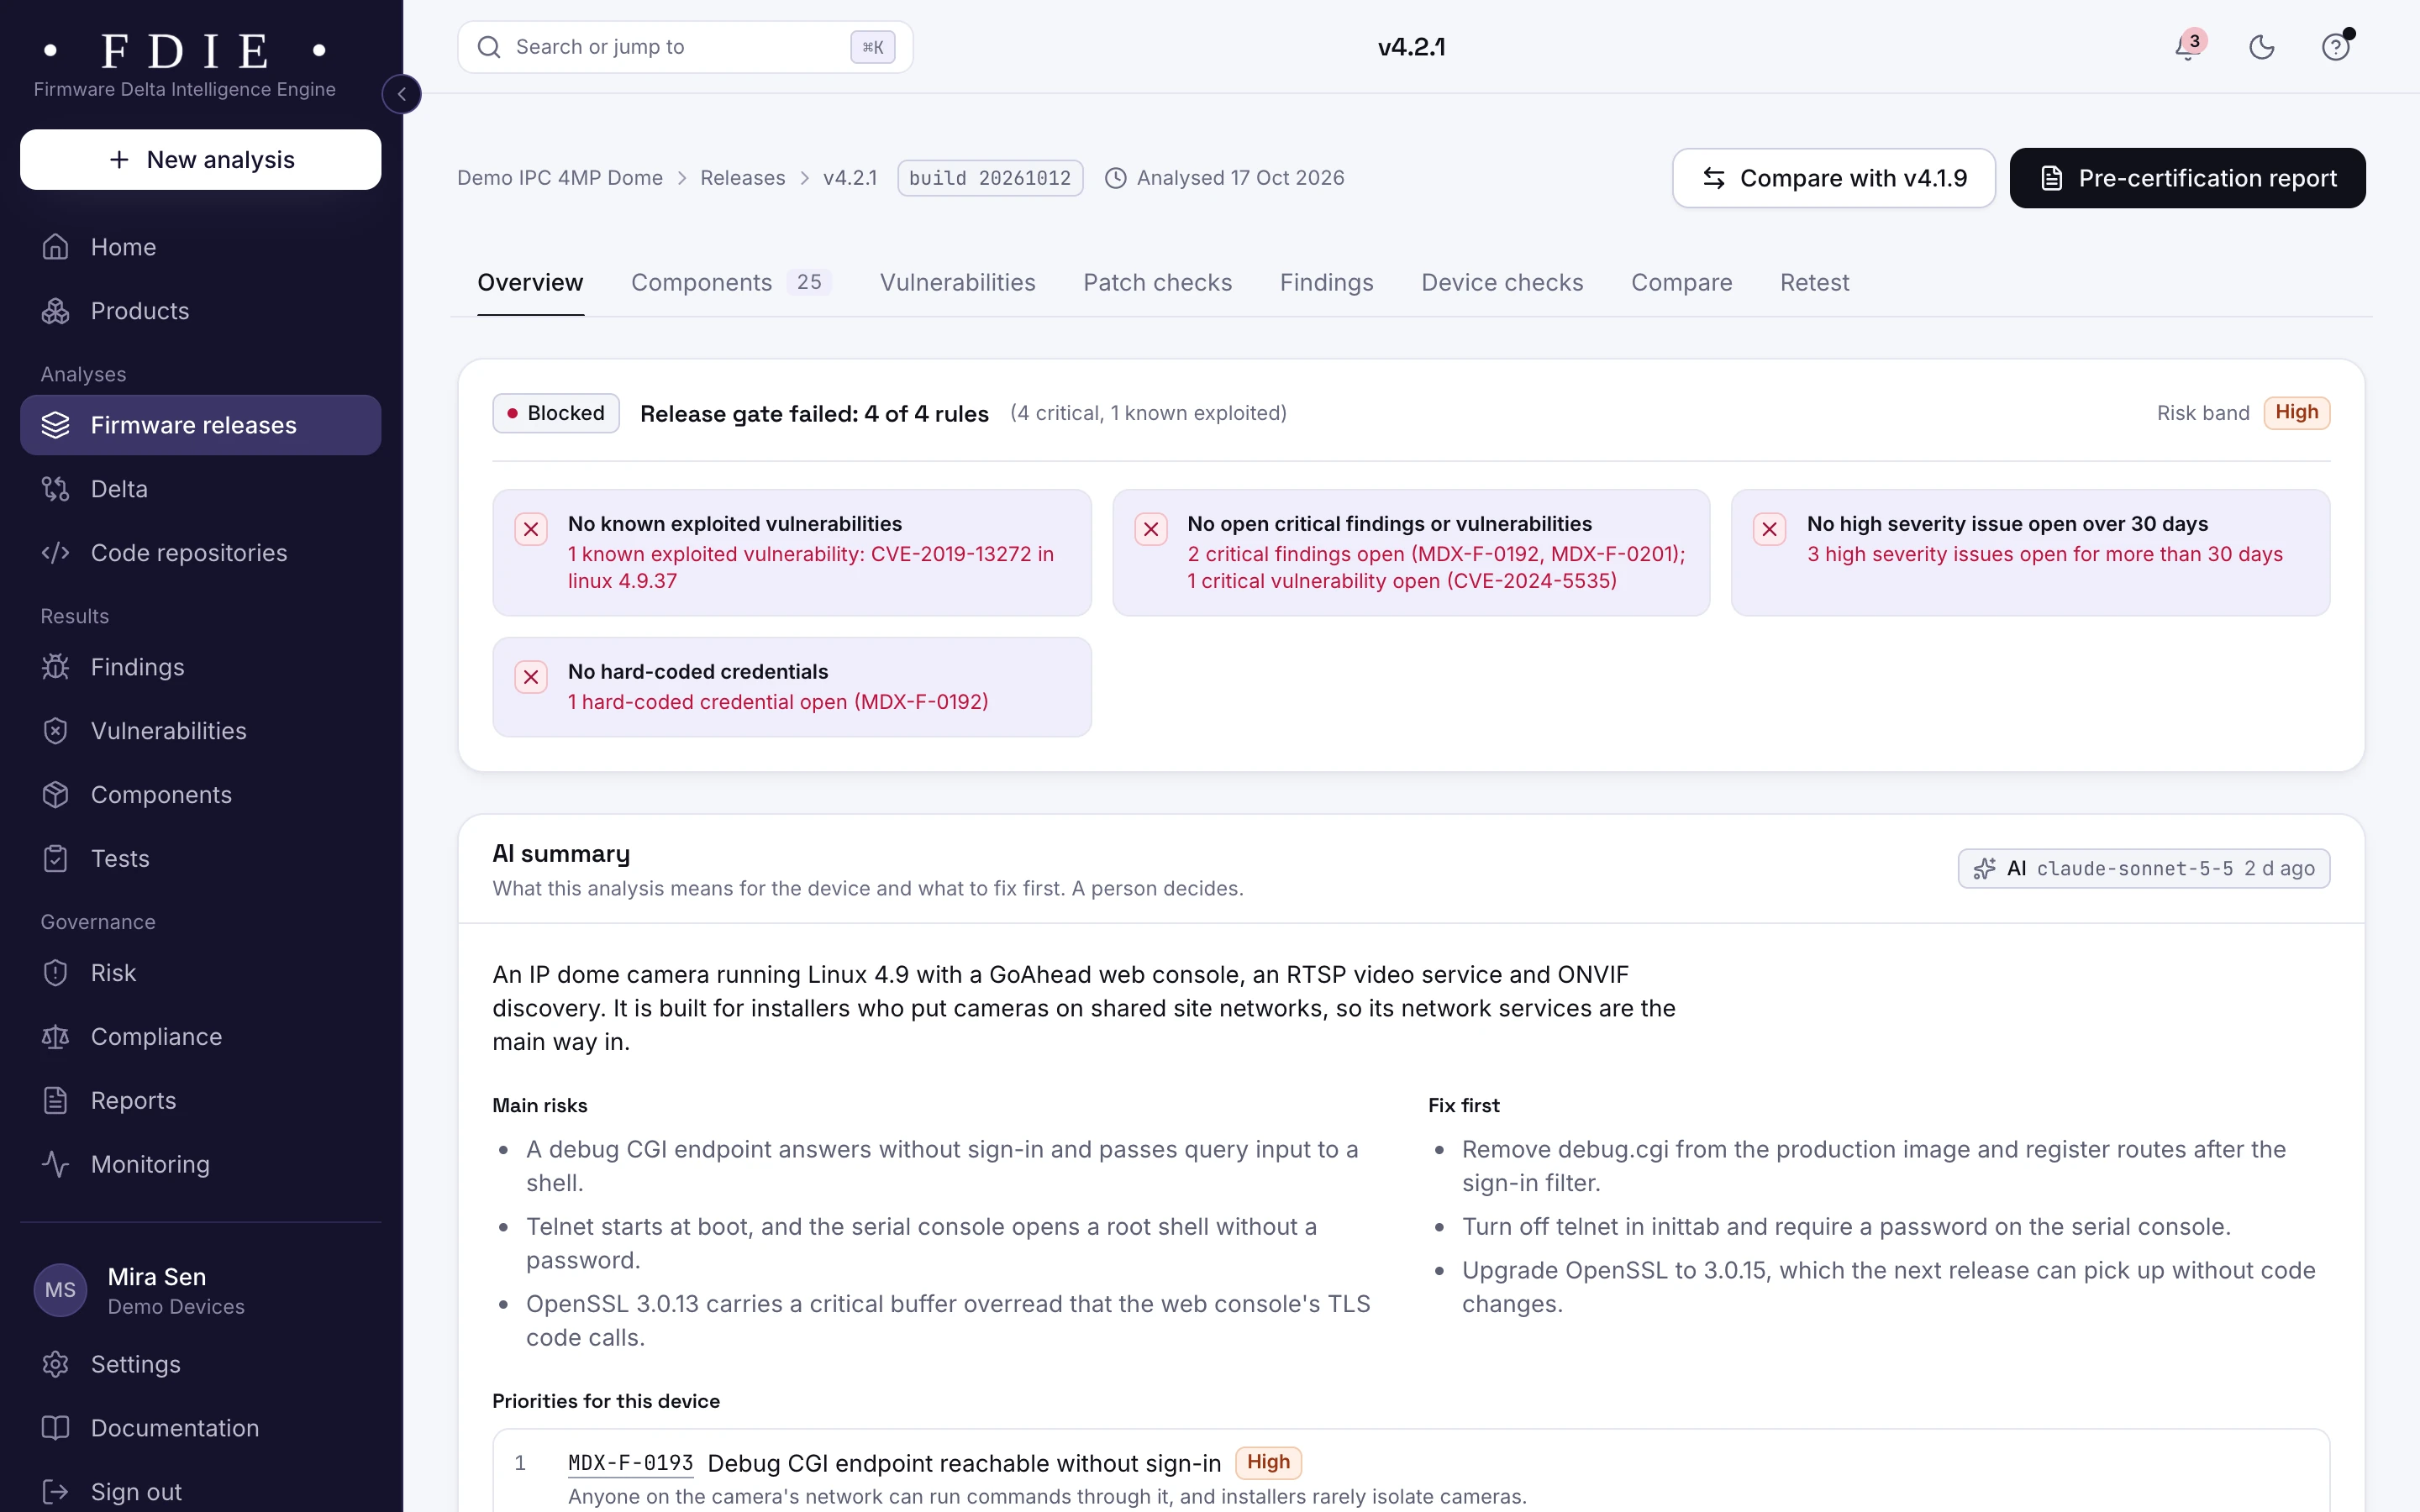
Stop finding failures at the lab
Every release is checked against your release rules before it leaves your team, with the reasons it would fail. What the analysis could not check is named, never counted as a pass.
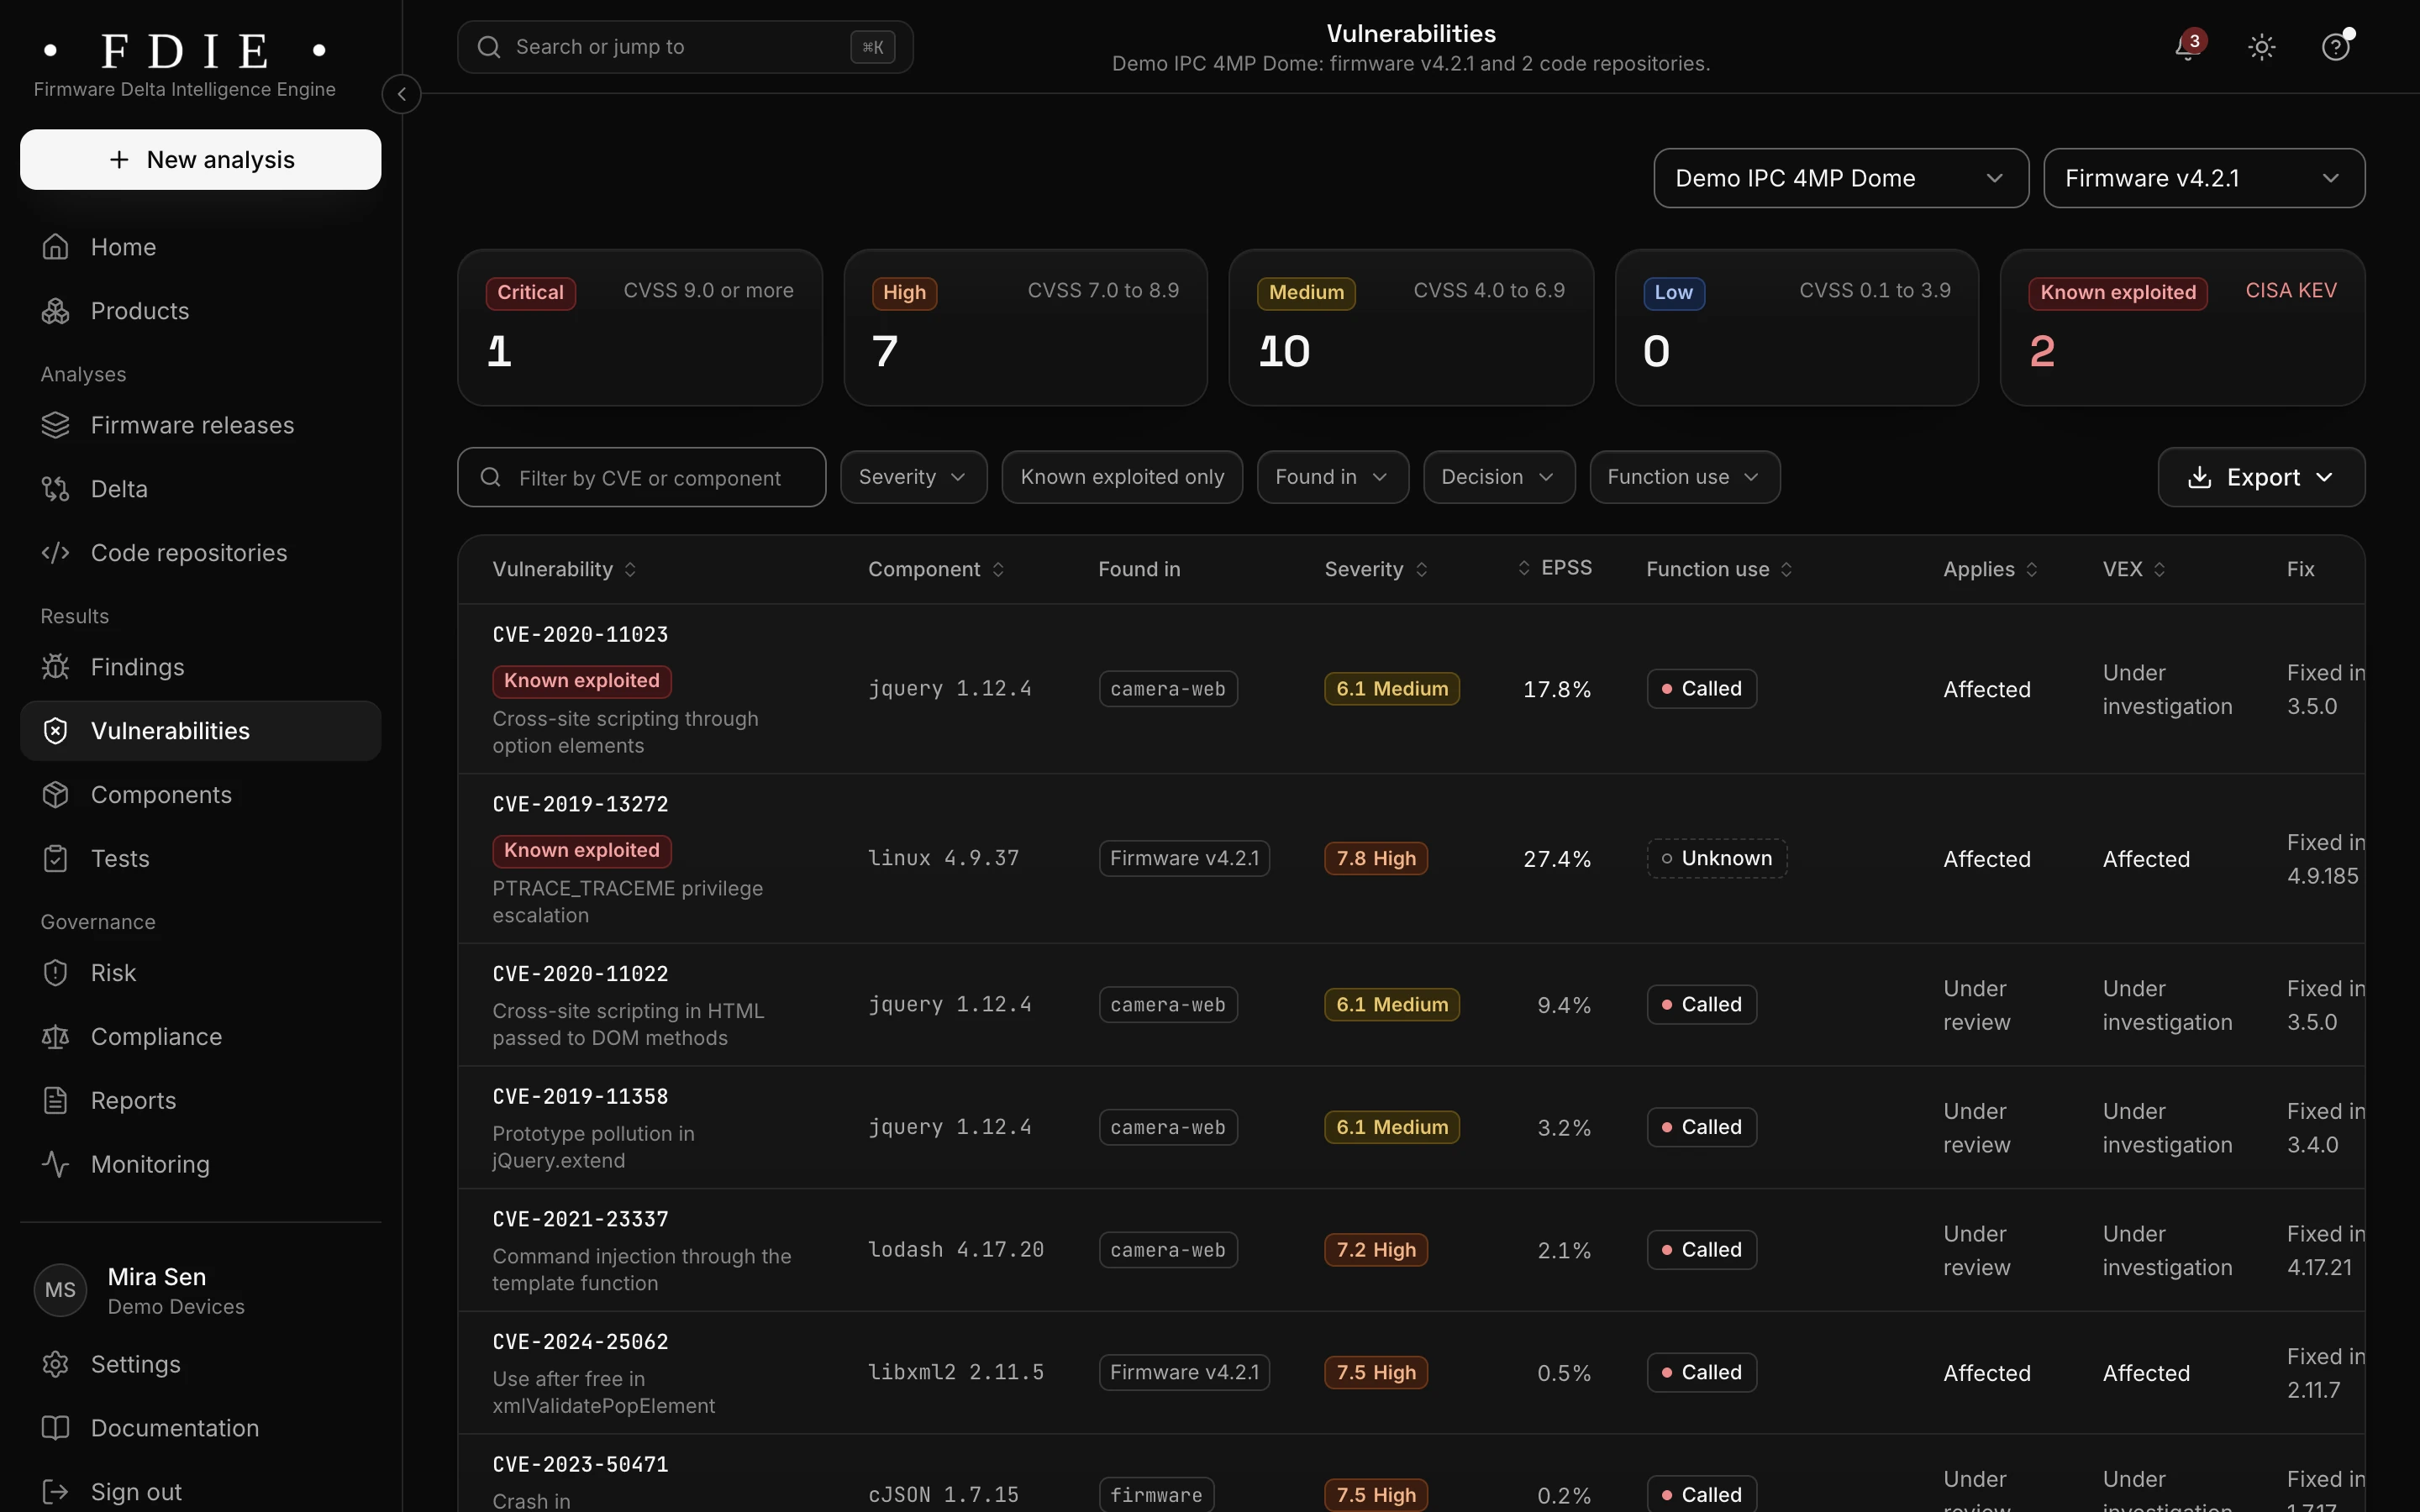
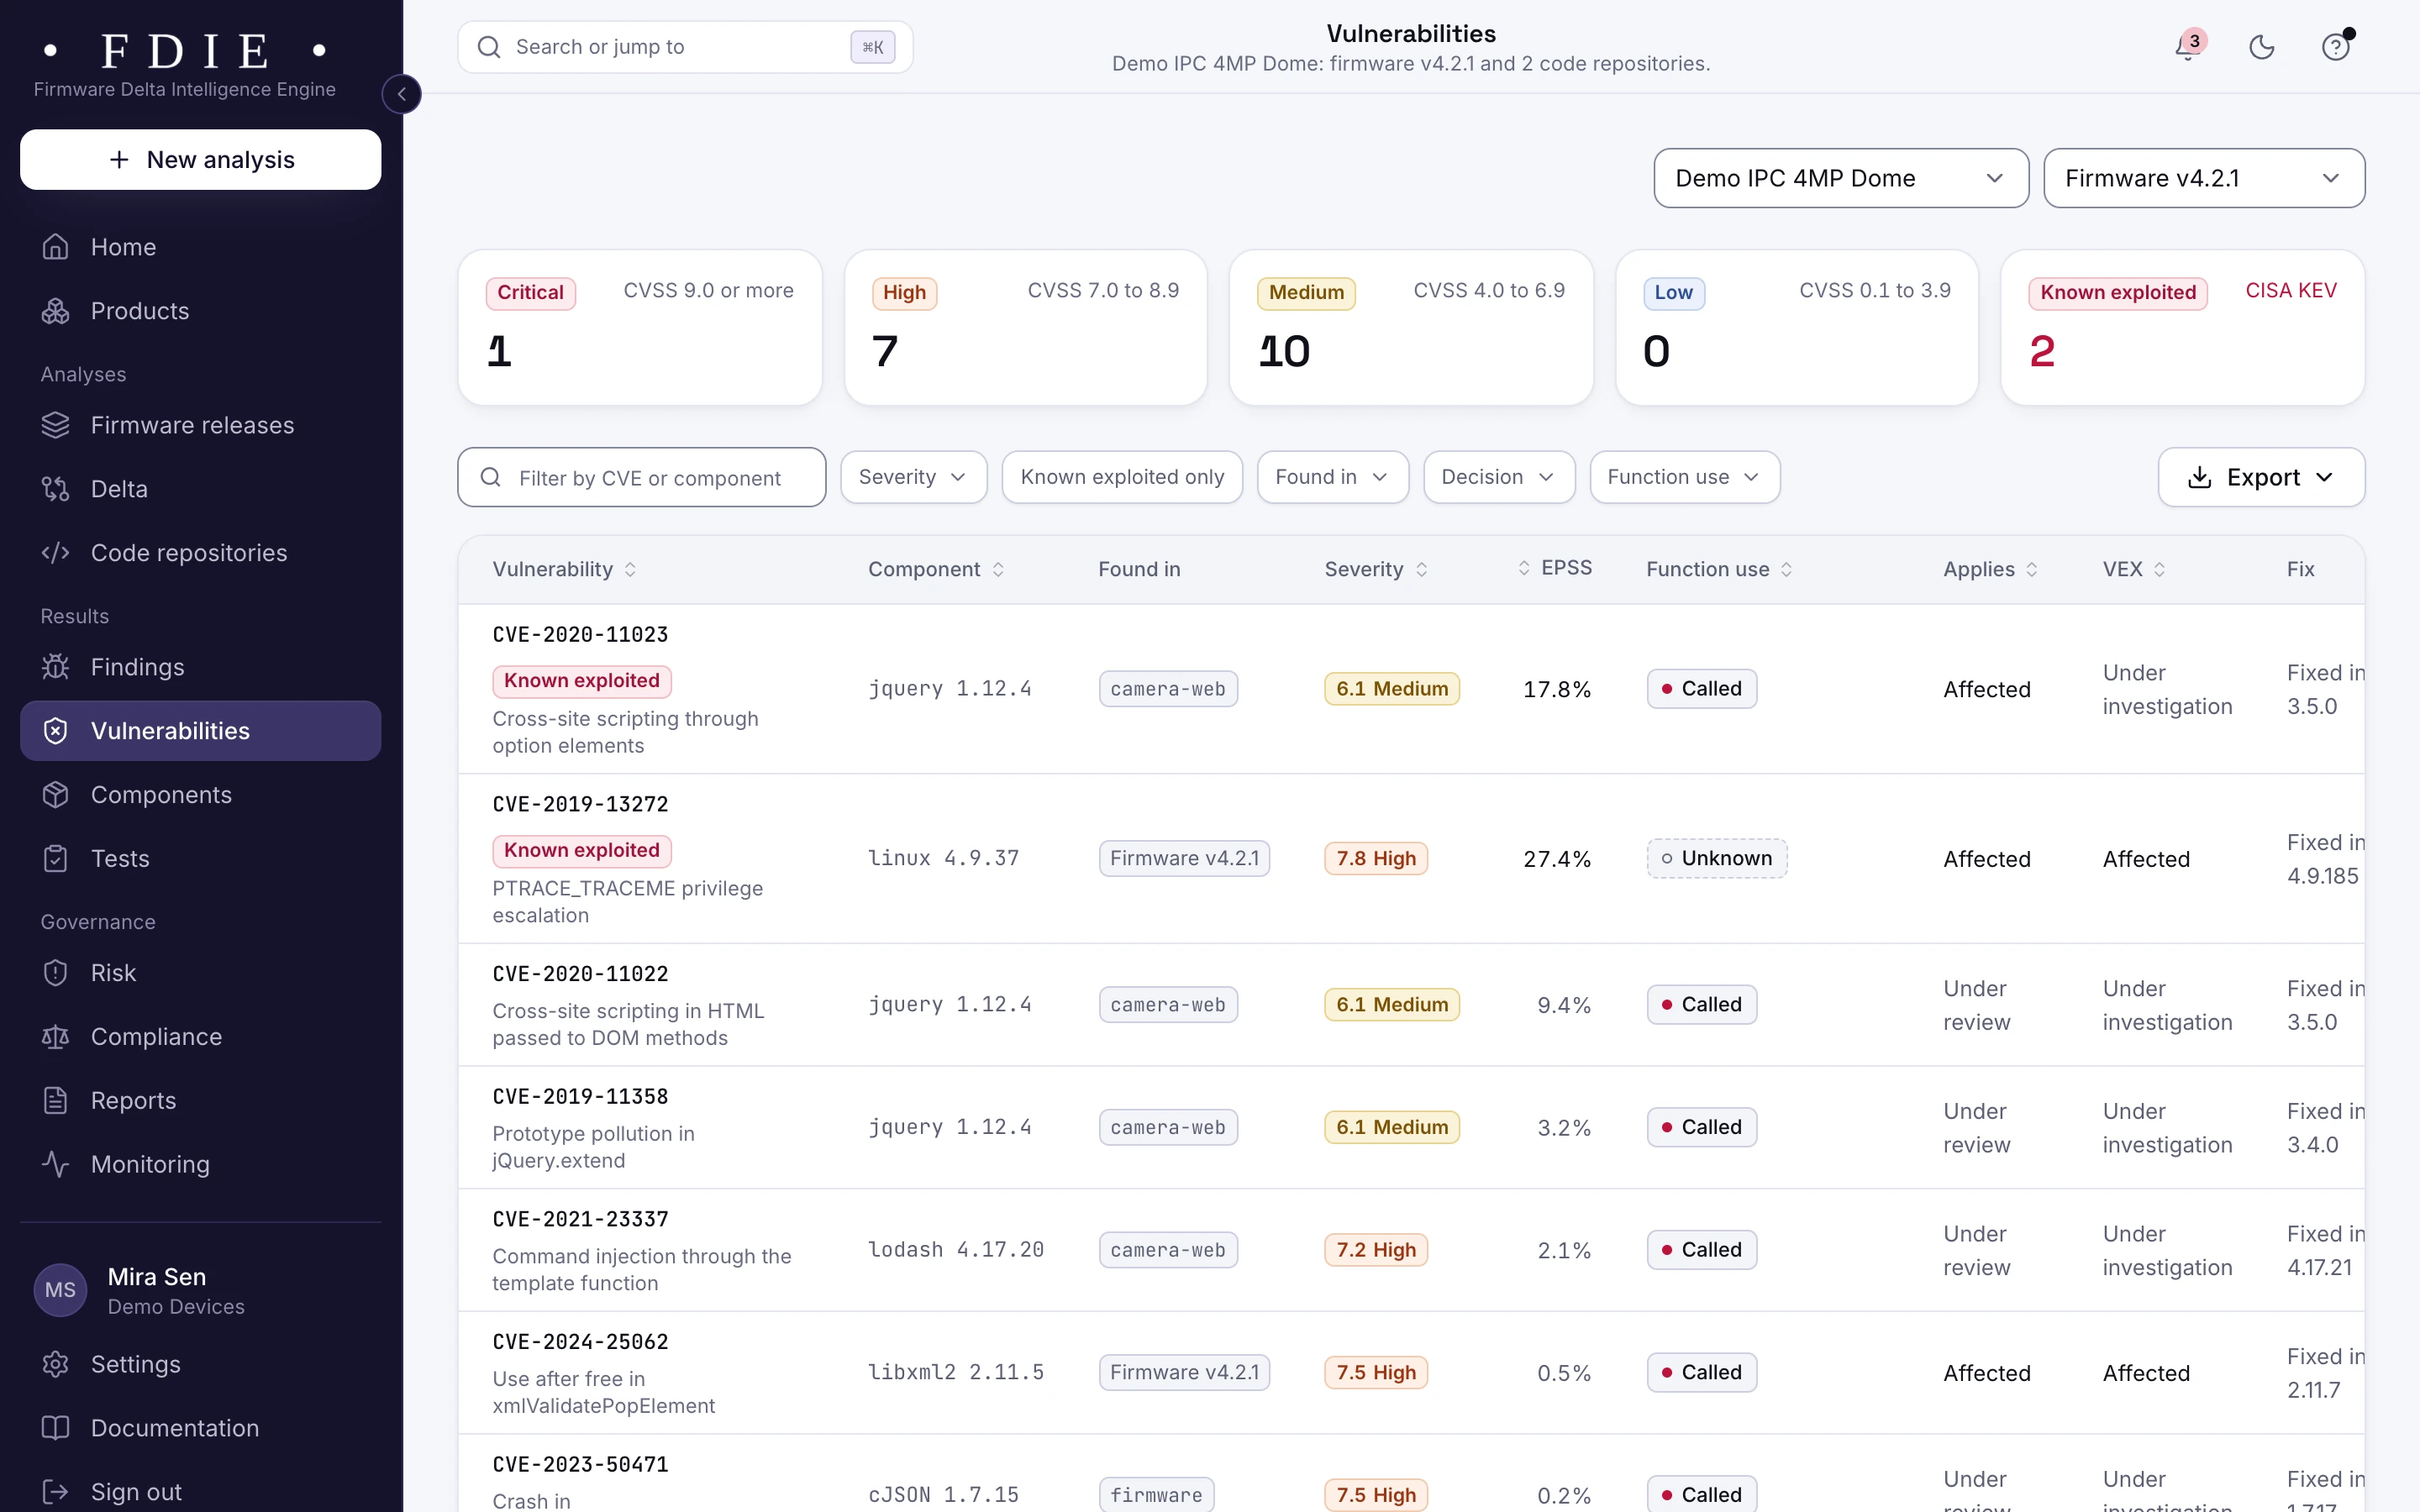
Know the day a flaw affects you
Components are matched to known vulnerabilities from NVD and OSV, the ones attackers already use first (CISA KEV), then by how likely they are to be exploited (EPSS), with whether your programs call the vulnerable code. Shipped releases are checked again every day.
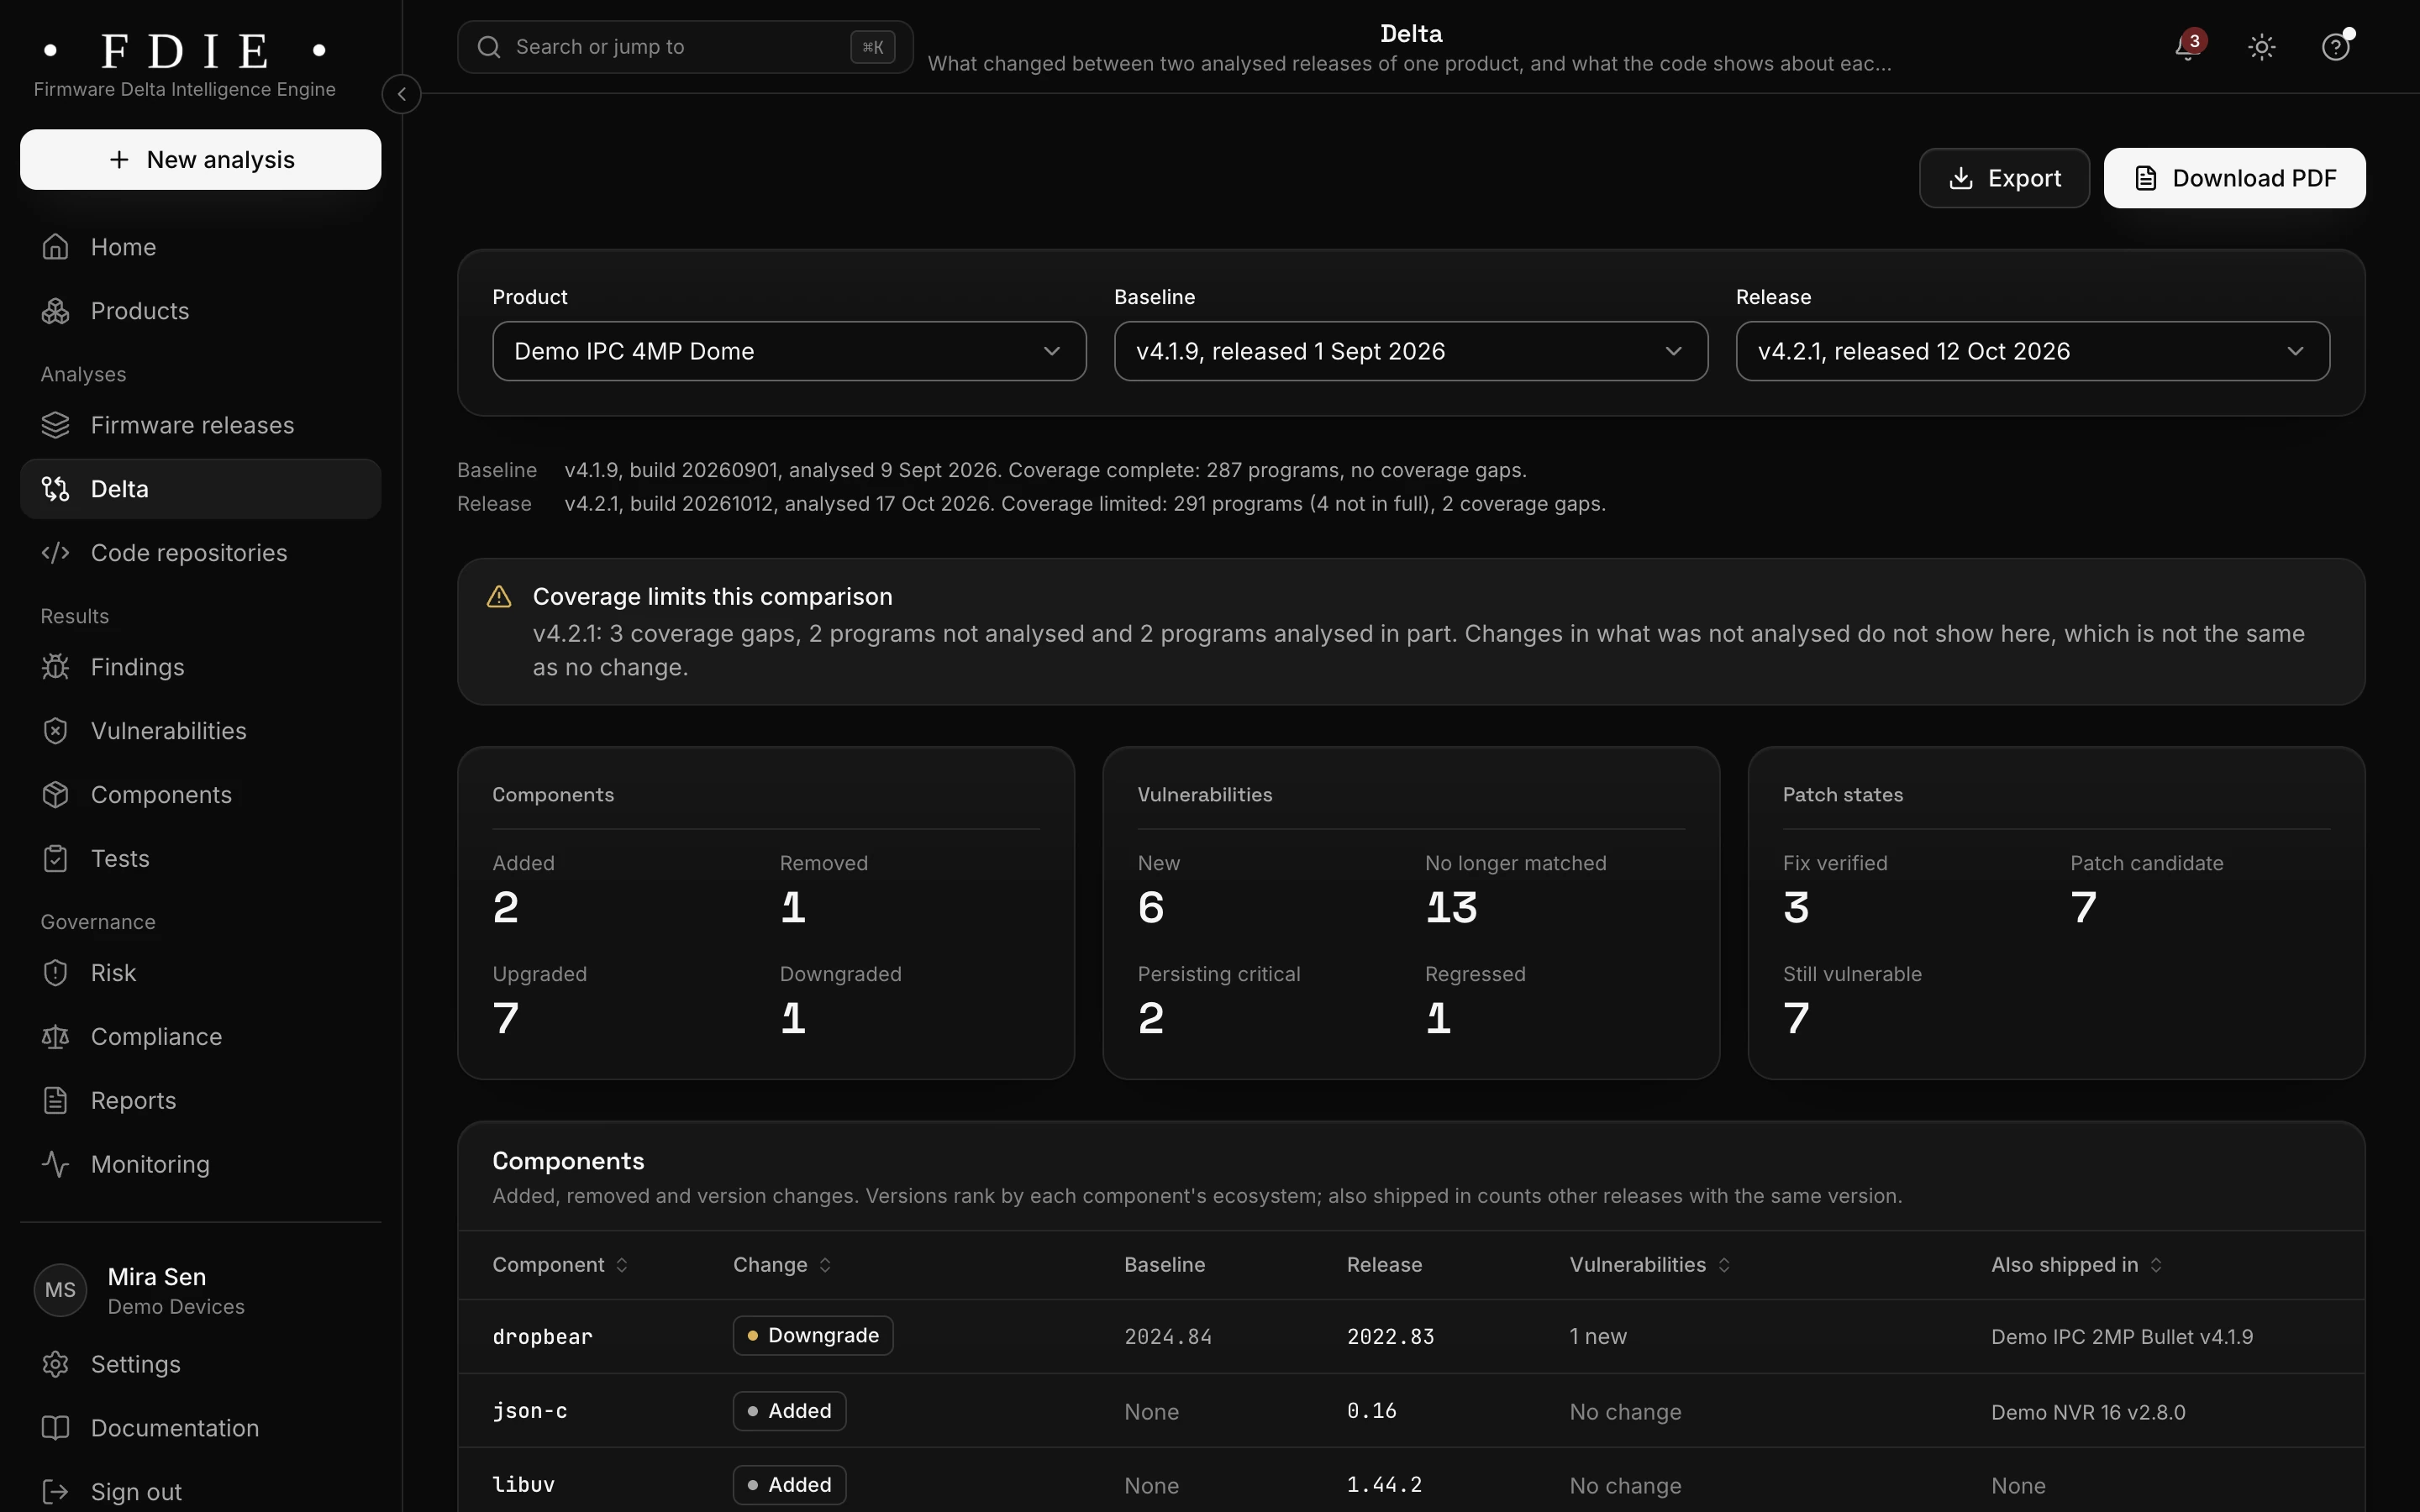
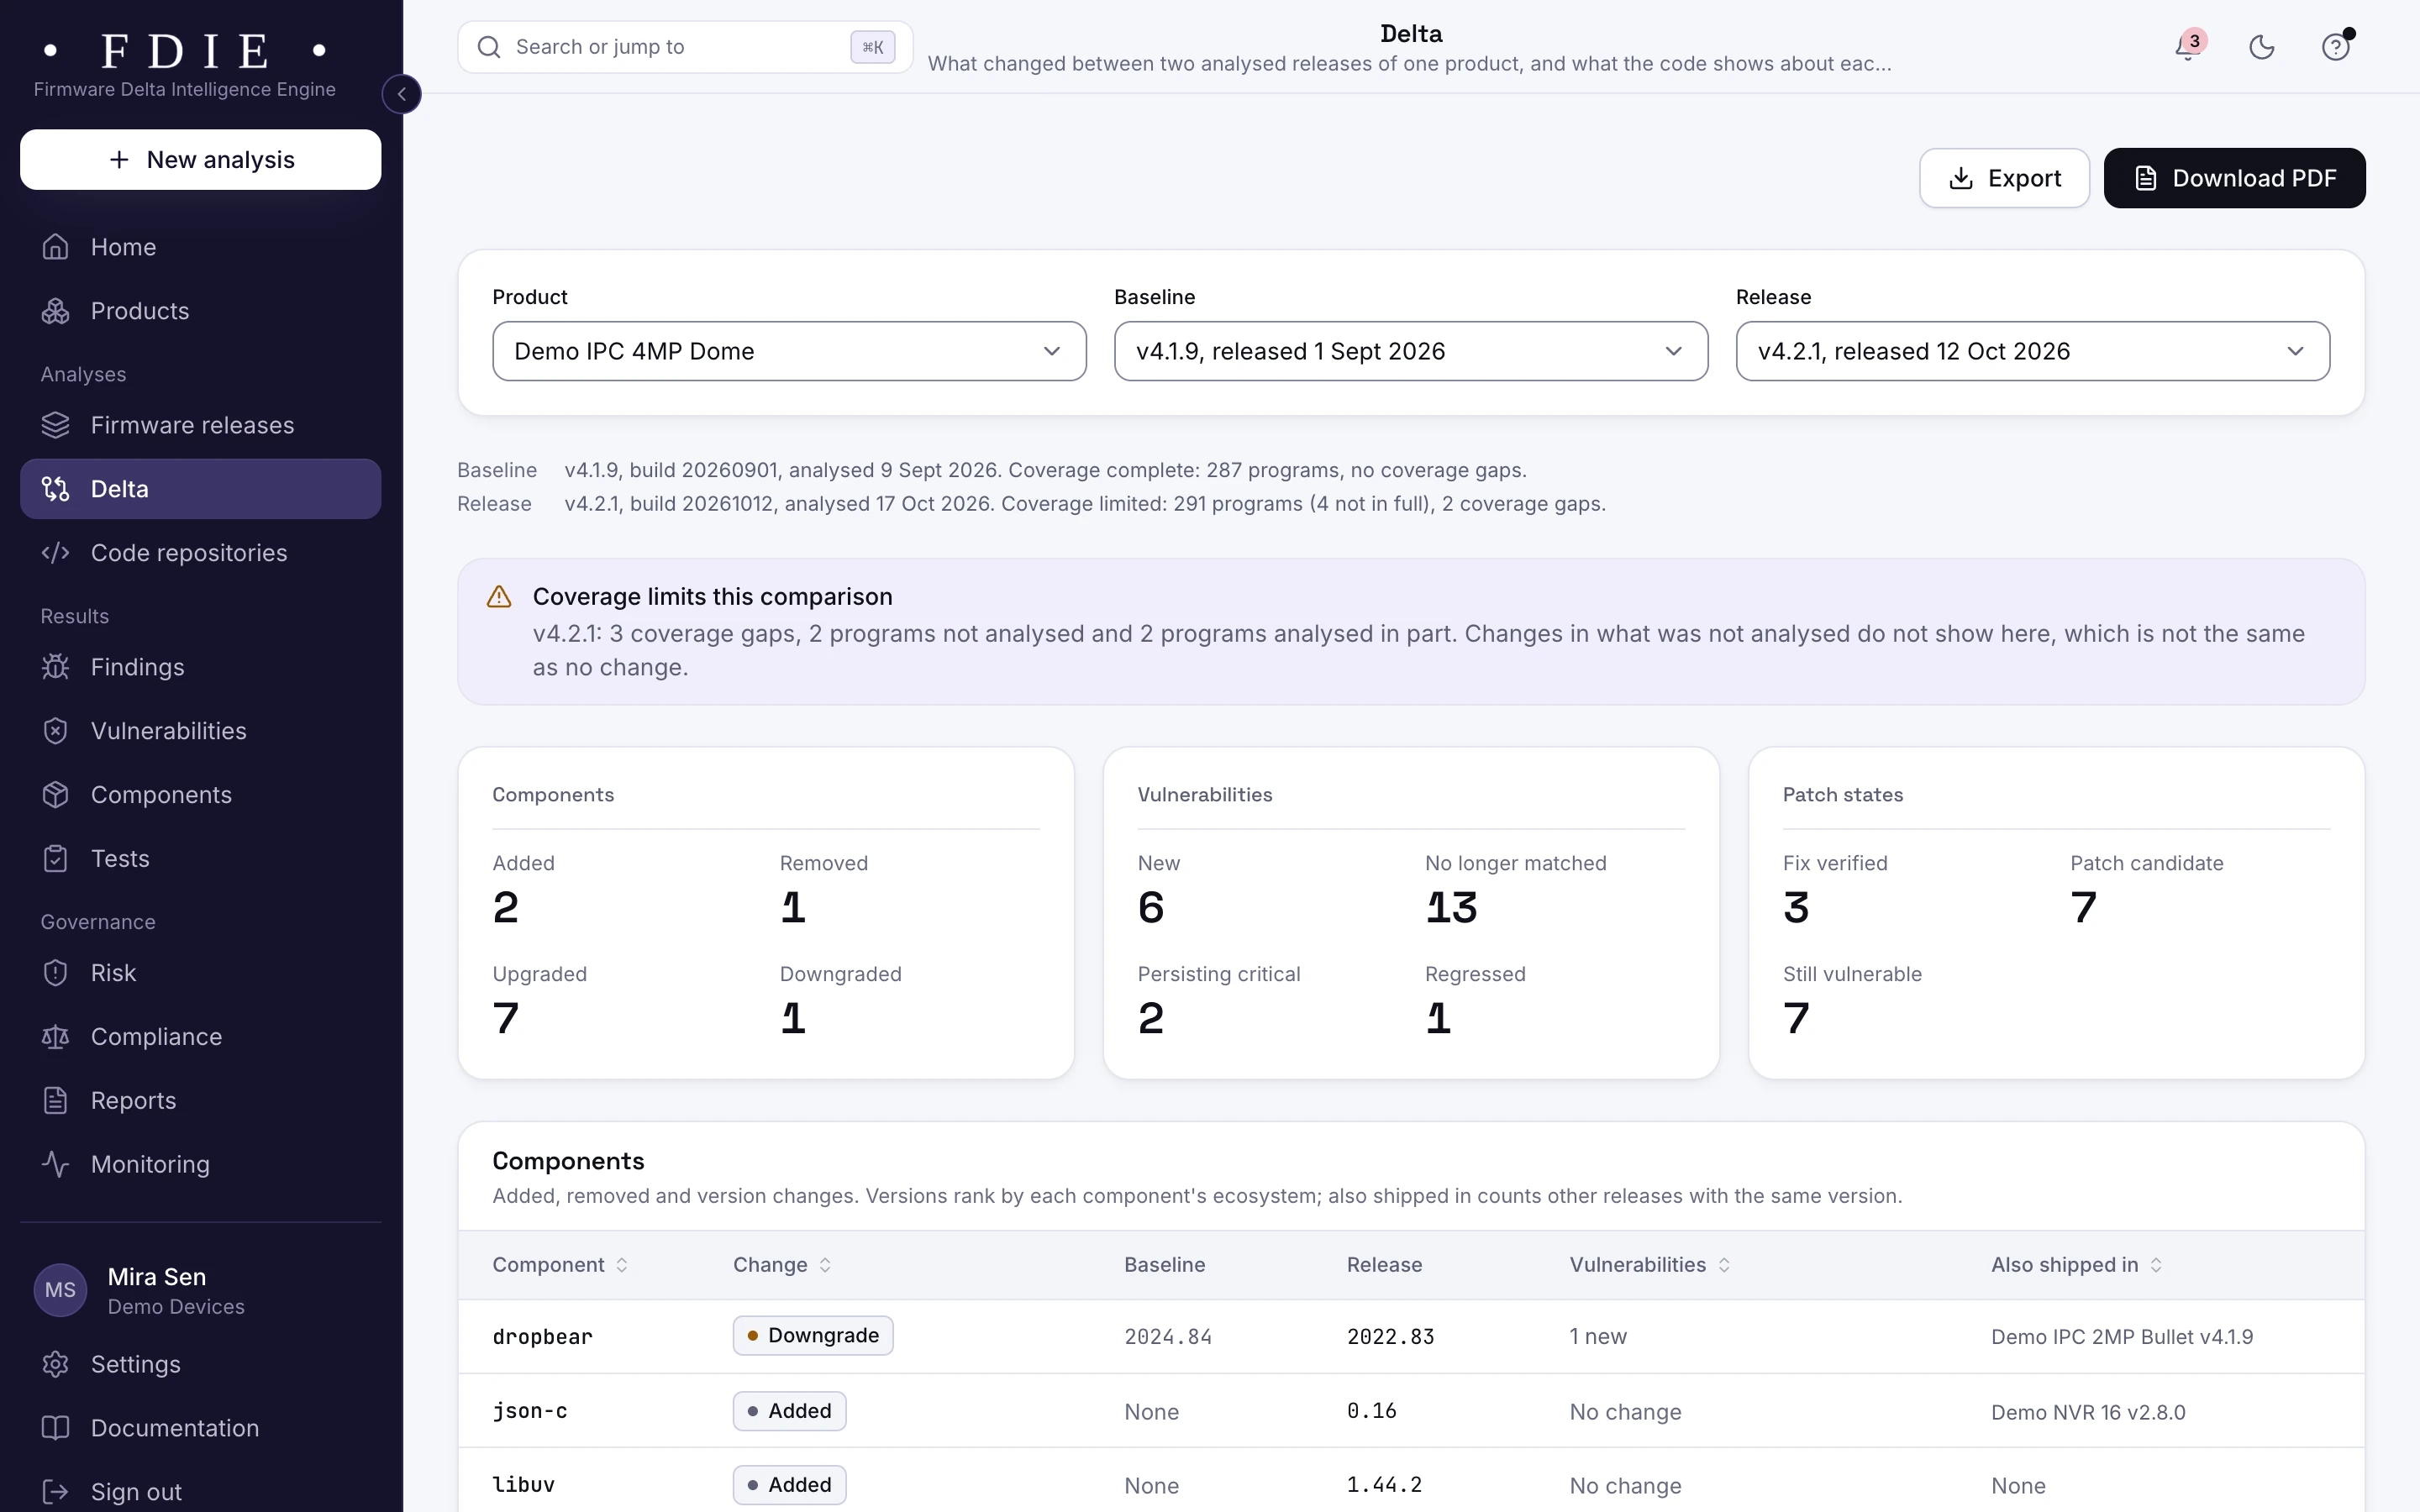
Prove an update fixed what it promised
Compare two releases: what was added, removed or upgraded, and whether each vulnerability is fixed in the code itself, even when the version string did not change. Share it as a delta report.
Evidence ready for the lab, the tender and the buyer
Each requirement of India's CCTV and router security rules, and of the other markets you sell in, with its status and the evidence behind it, for each analysed release.
India
- TEC 31318:2025
- MeitY ER-01
- NCCS ITSAR for IP routers
- NCCS ITSAR for Wi-Fi CPE
European Union
- EU Cyber Resilience Act, Annex I
- EN 18031-1
- EN 18031-2
- EN 18031-3
- prEN 40000 drafts
United States
- NIST IR 8425
- NIST IR 8259A
International
- ETSI EN 303 645
- IEC 62443-4-2
- OWASP FSTM
Fix faster with AI on your own key
Connect your own AI provider to explain findings, propose triage and suggest code fixes that a person opens as pull requests. Without a key, every result still comes from our rules and engines.
People decide
AI explains and proposes. It never changes evidence, and a person accepts or rejects every proposal.
Never trained on your data
Not by us, and not by anyone else.
How we work
Gaps named, never hidden
Formats we cannot read and programs past the time budget are listed as coverage gaps.
Two-step sign-in for everyone
Each organisation is kept apart in the database, and the audit log cannot be changed by the app.
An Indian company
MAGDOX Private Limited, founded in 2025 and led by Manish Sharma, Chief Executive Officer.
Find out what the lab would flag in your firmware
A 45-minute call with our team. Bring one firmware image.