Framework views
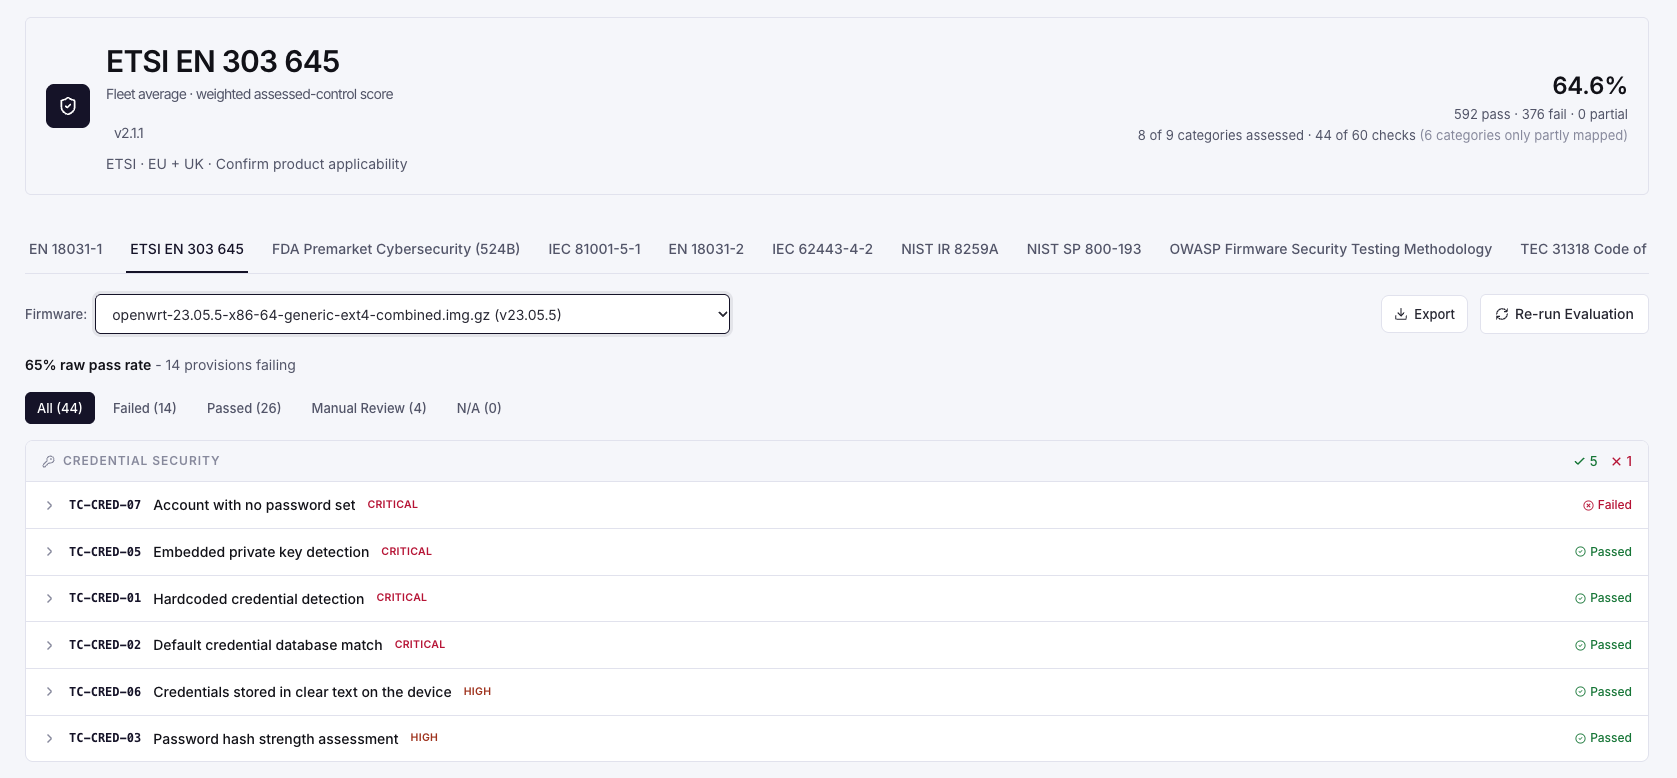
FDIE maps available technical checks to supported framework profiles. Confirm the applicable edition and product scope with a qualified reviewer. Scores weight assessed controls; unassessed and not-applicable checks are excluded from that score and remain visible in coverage. A raw pass rate and a weighted fleet score use different denominators.
Inventories and exports
| Artifact | Purpose | Review before sharing |
|---|---|---|
| CycloneDX / SPDX SBOM | Identified software and available dependency information | Component identities, versions, licence evidence, analysis scope and feed context |
| CBOM | Identified cryptographic assets | Algorithm / key evidence and incomplete recovery |
| VEX | Recorded vulnerability applicability and dispositions | Analyst rationale, affected product/release and unresolved uncertainty |
| Assessment / PDF reports | Findings and supporting technical checks | Audience, sensitive content, selected framework and limitations |
| TARA / EMB3D review | Candidate threat relationships from firmware evidence | Assets, trust boundaries, physical context and missing operational evidence |
CRA disclosure review
Use the separate disclosure workflow to record investigation, awareness time, decisions and official submission references. A CVE match or KEV entry alone does not determine reportability. The responsible manufacturer must assess its legal duties and submit through the applicable official channel. FDIE does not notify a regulator simply because a record is created, and it does not issue CRA conformity grades or certificates.
Prepare a recipient-ready evidence package
- Confirm the product, release and intended assessment scope with the recipient.
- Review the relevant framework version and individual check states, including manual, not-applicable and unassessed work.
- Select the appropriate SBOM, CBOM, VEX or report output. Check that the format includes the information the recipient actually needs.
- Validate each material applicability decision and its supporting reason before sharing VEX.
- Review the exported file for sensitive content and retain its image identity and assessment context with the handover.
A customer export becomes a separate copy. Apply your own storage, access and retention rules after download, and regenerate the record when its underlying assessment or decision changes.